Holders who keep assets on Scroll and later withdraw to Ethereum rely on the network’s proof checks to settle state roots and withdrawal roots. A ChainCatcher report published on November 11, 2026, at 21:55 (UTC+8) relayed Scroll’s account of a flaw in that check.
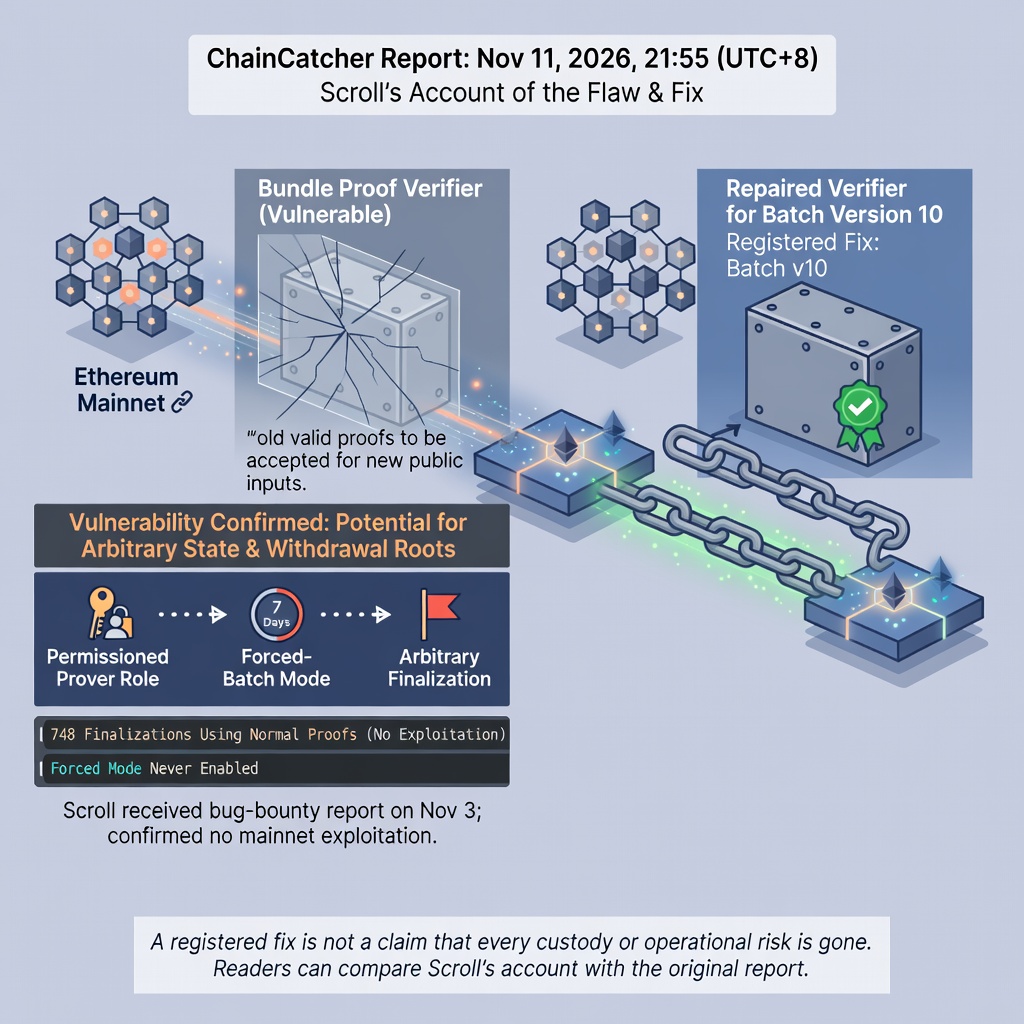
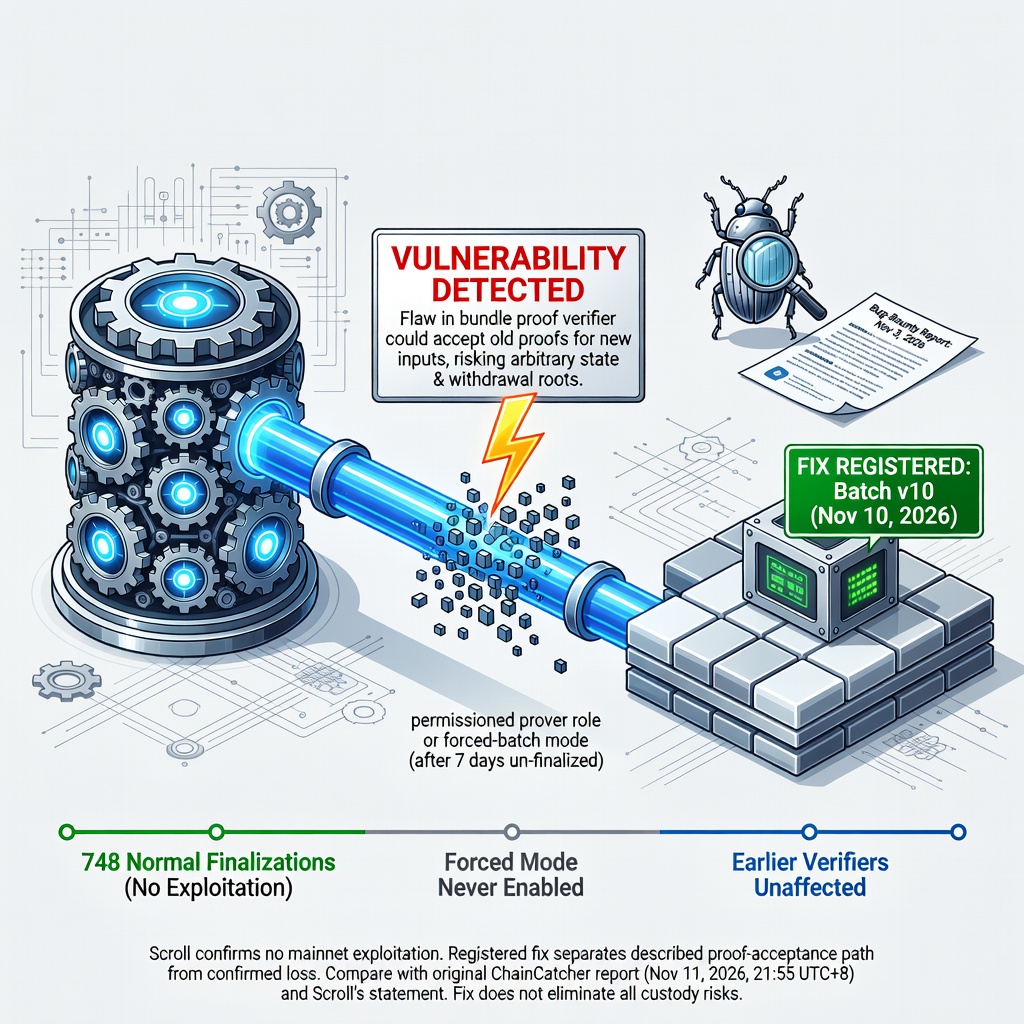
Scroll said it received a bug-bounty report on November 3 about a vulnerability in the bundle proof verifier deployed on Ethereum mainnet, and that on November 10 it registered a repaired verifier for batch version 10. Scroll said it had confirmed the vulnerability was not exploited on mainnet.
According to the report, the flaw could allow an old valid proof to be accepted for new public inputs, which could permit finalization of arbitrary state roots and withdrawal roots. Exploitation would require the permissioned prover role, or forced-batch mode, which opens only after seven days without finalization.
Scroll said forced mode was never enabled, that all 748 finalizations while the vulnerability was present used normal proofs, and that earlier versions of the verifier were not affected.
Those statements separate a described proof-acceptance path from any confirmed loss: Scroll reports no mainnet exploitation and a registered fix for batch version 10. Readers can compare that account with Scroll’s own statement and the original report. A registered fix is not a claim that every custody or operational risk is gone.
Original article: ChainCatcher