For anyone holding assets through a smart contract, this case illustrates a custody risk that is easy to miss: a valid signature does not necessarily make the action it authorizes safe. In an analysis published on May 14, 2026, SlowMist reported that an attacker used their own valid signature to change a ShapeShift FOX Colony contract’s routing configuration on Arbitrum, then used that control to move assets out of the contract. The report places the attack in May 2026 but does not give a more precise attack date.
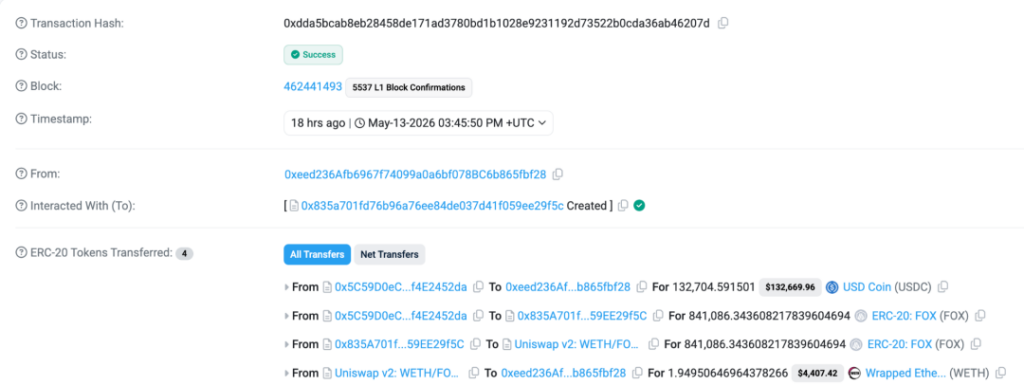
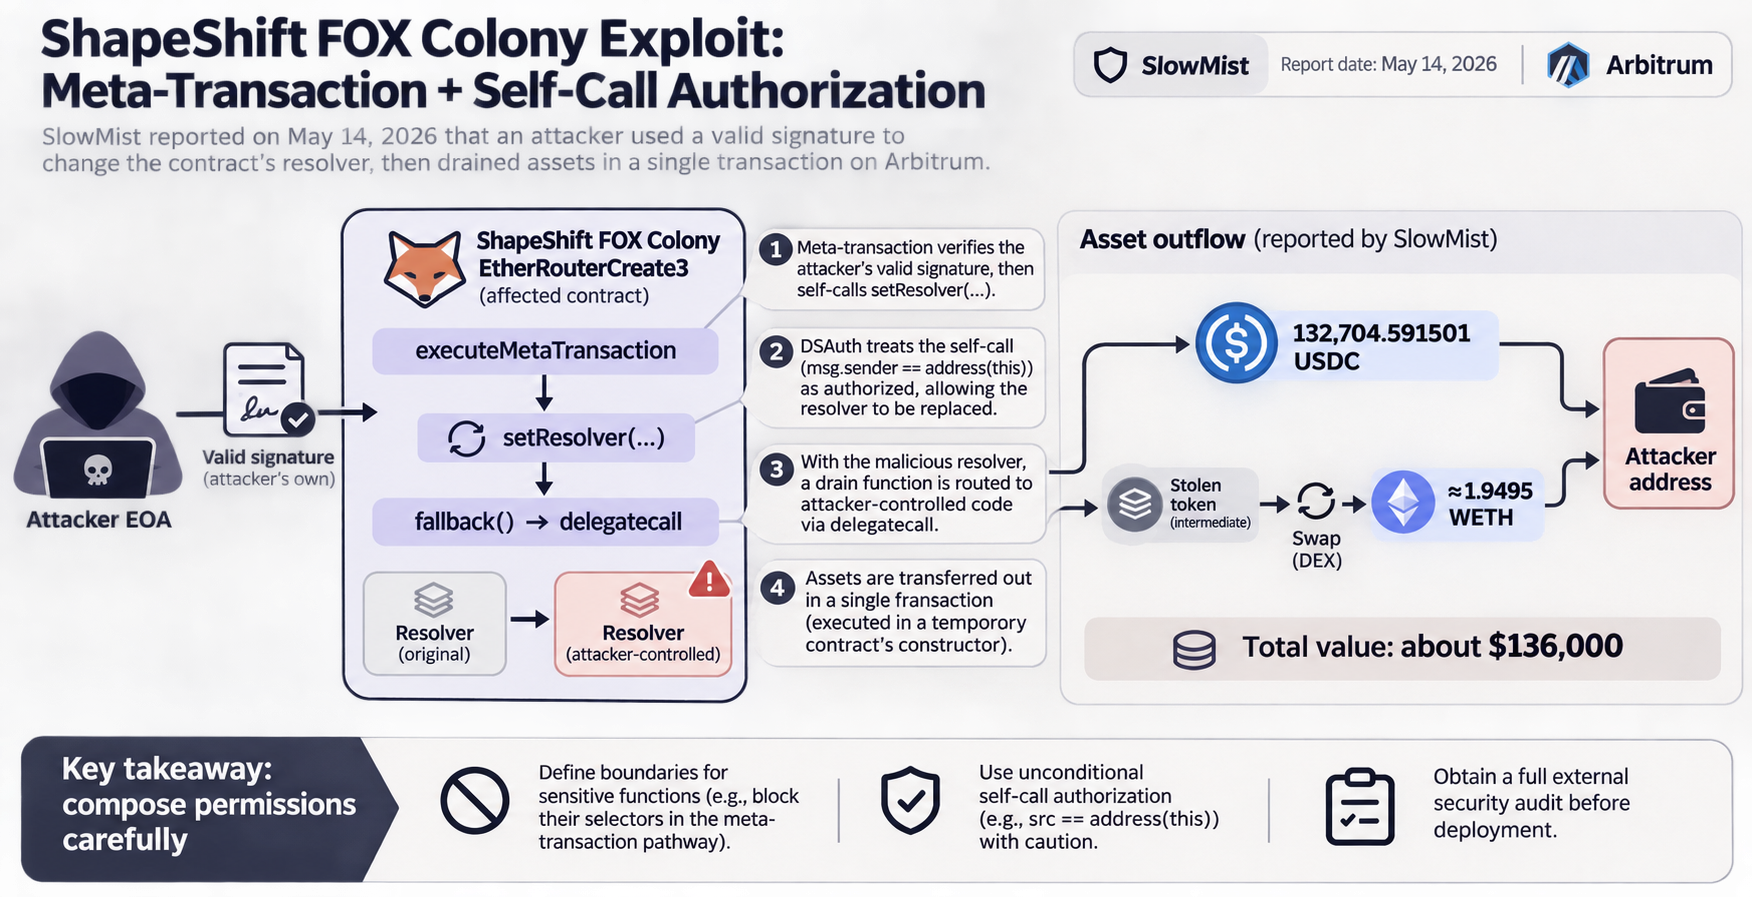
SlowMist reported proceeds of 132,704.591501 USDC and approximately 1.9495 WETH, worth about $136,000 in total. It described the exploit as a single transaction, with the attack sequence executed in a temporary contract’s constructor.
Where the trust boundary failed
The affected EtherRouterCreate3 contract used a resolver to choose which implementation should handle functions that the router did not implement directly. Its executeMetaTransaction function verified a user’s signature and then called the router itself with the signed function data. According to SlowMist’s analysis of a decompiled, unpublished implementation, that function did not exclude sensitive calls such as setResolver.
The attacker signed a call to replace the resolver with an attacker-controlled one. The signature check passed because the signature was the attacker’s own—not a forgery. But when the meta-transaction made the internal call, the protected setResolver function saw the caller as the router itself. The router’s DSAuth authorization logic automatically trusted calls from its own address, allowing the resolver change.
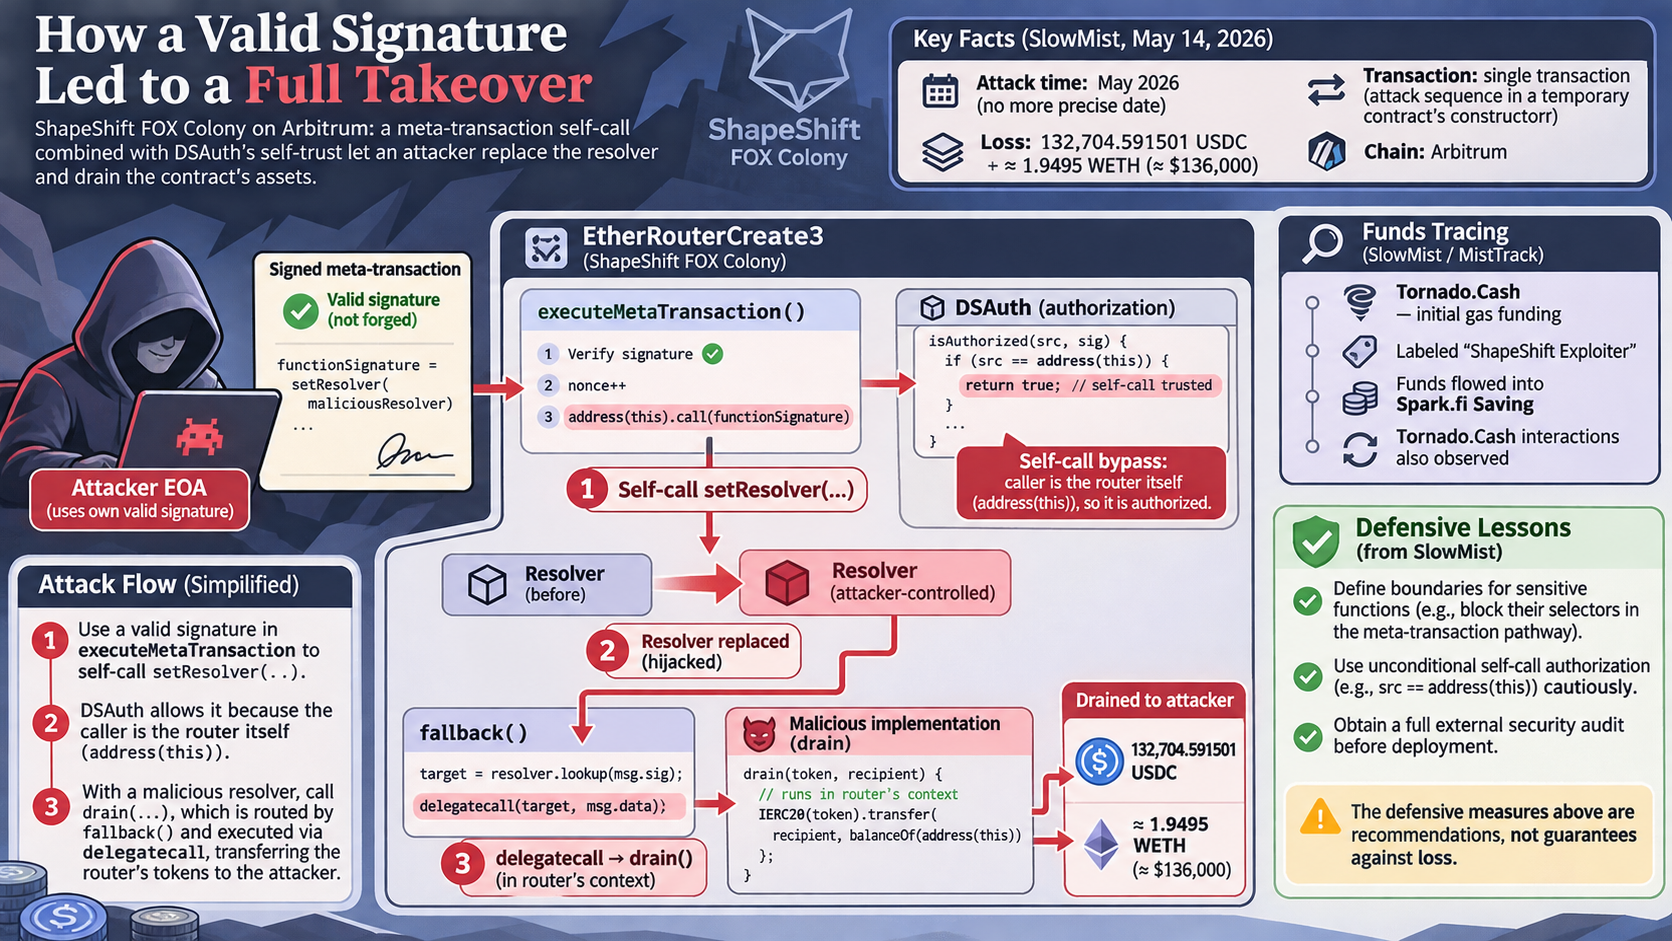
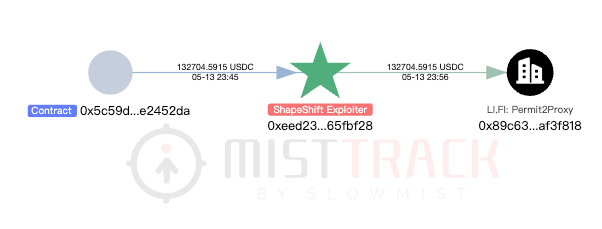
With the resolver replaced, a call to a drain function was routed to attacker-controlled code. The router executed that code by delegatecall, so it ran in the router’s context and could transfer tokens held by the router. SlowMist reported that 132,704.591501 USDC went directly to the attacker’s address. It said another token taken from the contract was swapped for 1.949506469643782660 WETH, which also went to that address.
What the report says about the funds
SlowMist said its MistTrack analysis linked the attacker address to initial gas funding from Tornado.Cash, labeled it “ShapeShift Exploiter,” and observed funds flowing into Spark.fi Saving as well as Tornado.Cash interactions. These are SlowMist’s reported tracing findings, not a claim that the funds have been recovered.
The defensive lesson is about composing permissions, not simply checking signatures. A meta-transaction pathway that accepts arbitrary function calls can undermine an authorization rule that trusts every self-call. SlowMist recommends defining boundaries for sensitive functions—including blocking their selectors in the meta-transaction pathway—using unconditional self-call authorization cautiously, and obtaining a full external security audit before deployment. None of those measures, on its own, should be treated as a guarantee against loss.