For people holding KAVA or using HARD Lend, the key distinction is where Kava says the breach occurred: in the lending application, not in Kava Chain’s underlying consensus system. In an update reported on November 16, 2026, Kava said an attacker removed about 53.9 million KAVA, worth approximately $1.83 million, from HARD Lend’s lending pool.
According to Kava’s security update, the attacker exploited an accounting flaw in a dormant BUSD collateral market. By inflating the collateral value recorded in a lending account, the attacker repeatedly borrowed and liquidated positions, draining available pool liquidity.
The report said on-chain data showed that about 49.2 million KAVA, or 91.28% of the tokens taken, were moved to BNB Chain through LayerZero and sold. Kava said it had blocked further outflows and that some funds had been frozen at centralized exchanges and bridging endpoints as of November 16. Contributors were working with security teams, trading platforms and law enforcement to trace and seek recovery of the funds.
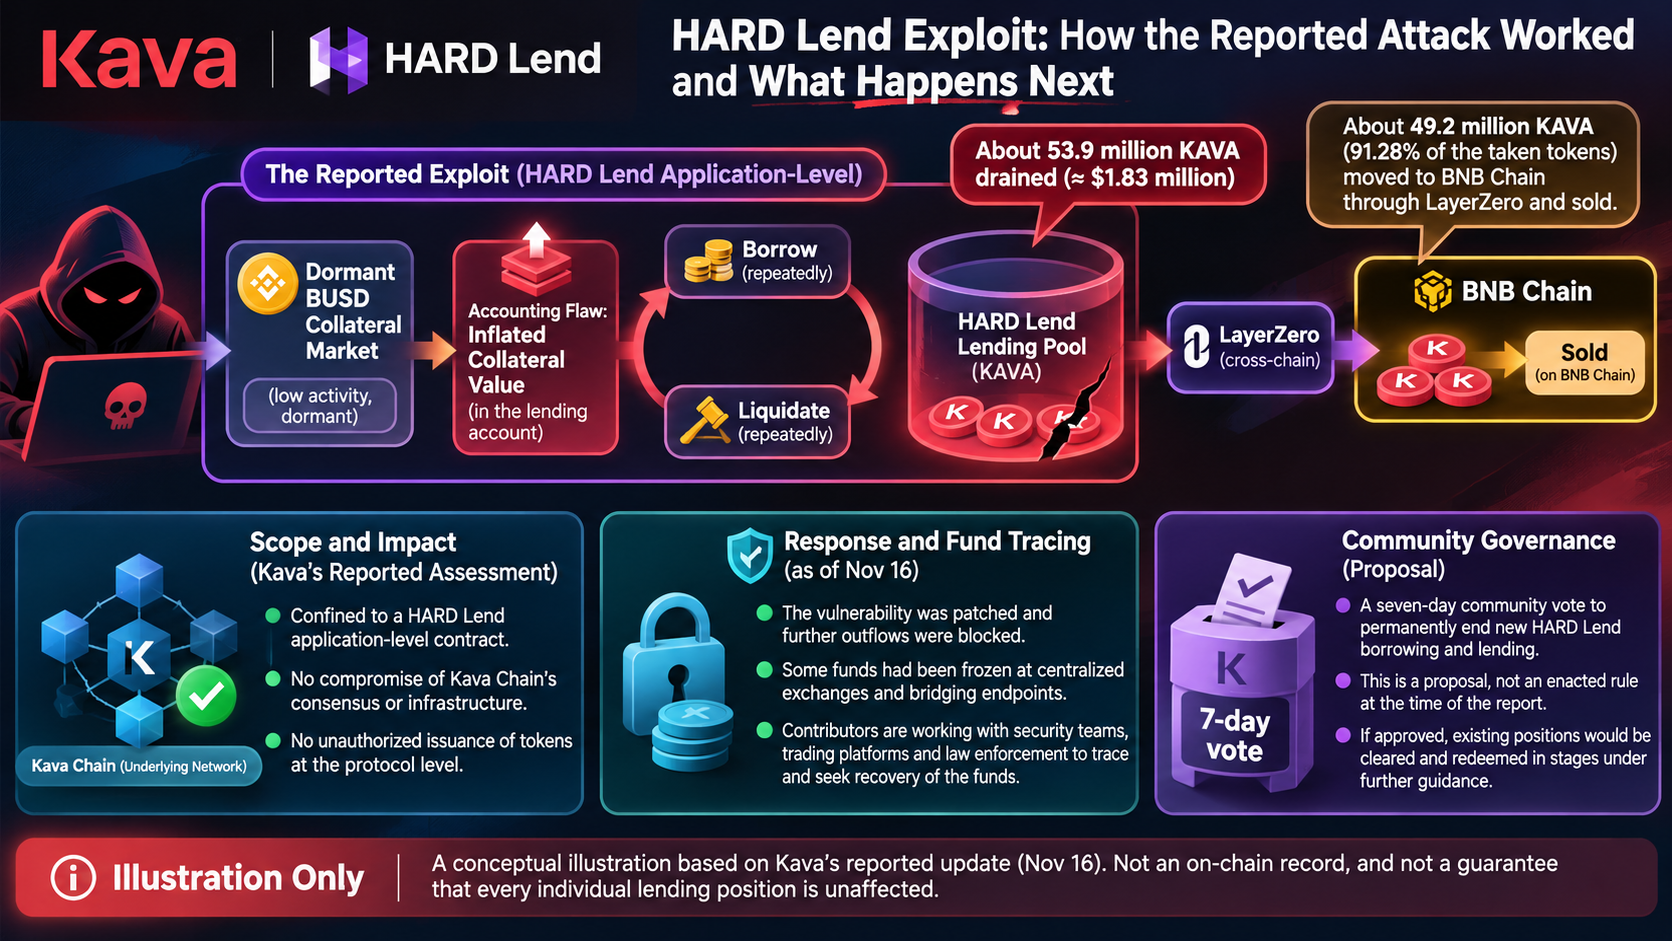
Kava said the incident was confined to a HARD Lend application-level contract. It reported no compromise of chain consensus or infrastructure and no unauthorized issuance of tokens at the protocol level. Those statements describe Kava’s reported assessment, not a guarantee that every individual lending position is unaffected.
Kava also opened a seven-day community governance vote on permanently ending new HARD Lend borrowing and lending. That shutdown was a proposal, not an enacted rule at the time of the report. If approved, existing positions would be cleared and redeemed in stages under further guidance.