A familiar website is not, by itself, a guarantee that a wallet address copied from it is safe to use. In a campaign reported on November 17, 2026, attackers placed malicious code in website scripts associated with 178 organizations, according to an investigation by Report URI. The code could replace a copied cryptocurrency address with one controlled by the attackers, creating a risk for anyone who pasted that address into a transfer.
The affected organizations included Ledger, OANDA/Coinpass, IG, Interactive Investor and TMS Brokers, as well as the BBC, CNN, IKEA, Salesforce and Zoom. Researchers also found code designed to capture card details entered into certain website forms. These capabilities do not establish that every visitor was affected or that funds or card details were stolen.
How the script reached visitors
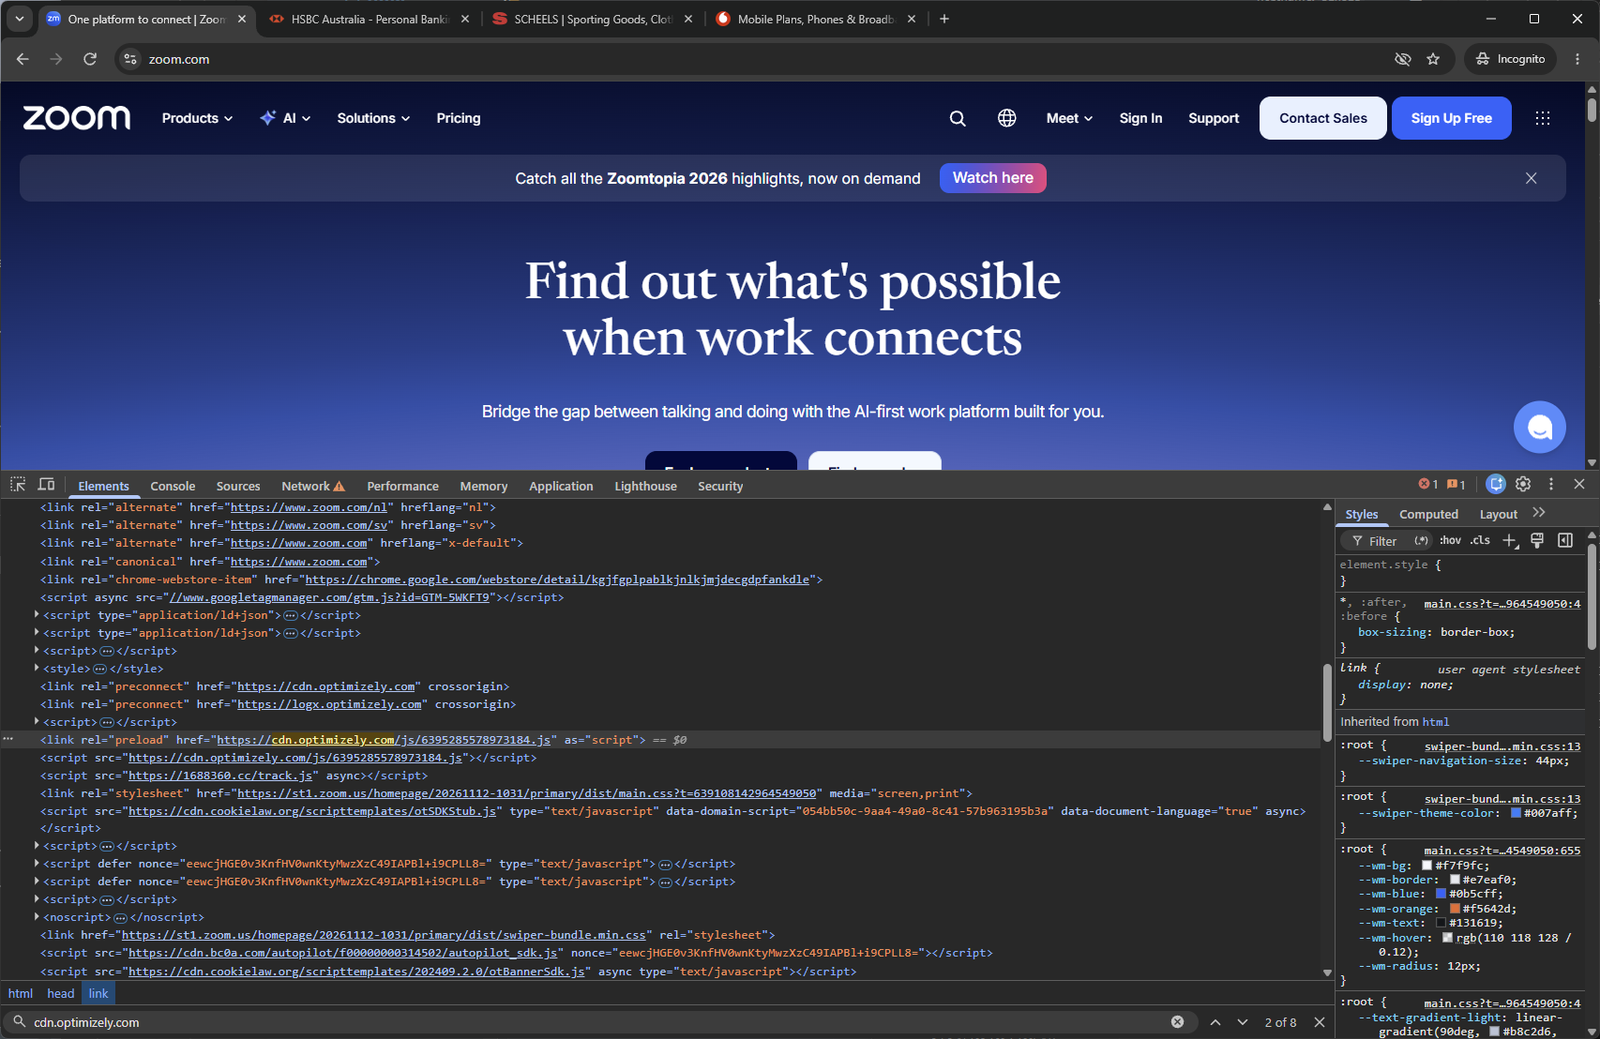
Optimizely, a platform that lets businesses run website experiments and custom JavaScript, said an unauthorized party exploited a vulnerability in its Experimentation account signup flow to add malicious code to some customer projects. Otherwise legitimate scripts could then load that code when visitors opened affected pages.
Optimizely said it blocked the vulnerable path, deployed a fix, removed injected code, ended active sessions, revoked tokens and reset access for affected accounts. It also said it blocked code delivery in Cloudflare, notified affected customers and continued investigating. Researchers had not established how the attackers gained access to modify the projects.
According to Report URI CEO Scott Helme, the BBC was among the first sites observed serving the injection at 4:21 am UTC on November 16. By 9:52 pm UTC that day, one of 188 infected snippets still contained malicious code; Ledger’s snippet had been cleaned at about 8:41 pm UTC. The 188-snippet count is distinct from the 178 organizations whose scripts were affected.
What the code could—and could not—access
The address-replacement code could change a cryptocurrency address copied to a visitor’s clipboard. Someone who did not check the address after pasting it might then send funds to the attacker instead of the intended recipient. The practical check supported by this incident is to verify the destination address in the wallet before approving a transfer, even when the address came from a trusted-looking site.
StepSecurity reported that another part of the script watched for card numbers, expiry dates and security codes entered into website forms and sent captured details to an attacker-controlled server. It could not read payment fields isolated in a third-party provider’s cross-origin frame. Helme said researchers had no evidence that payment cards were actually captured; he described the risk as concentrated on sites collecting card numbers in their own forms during the affected period. Helme also reported that the script loaded code linked to the Coruna and DarkSword iOS exploit kits for visitors using iPhones and iPads.
Loss figures remain uncertain
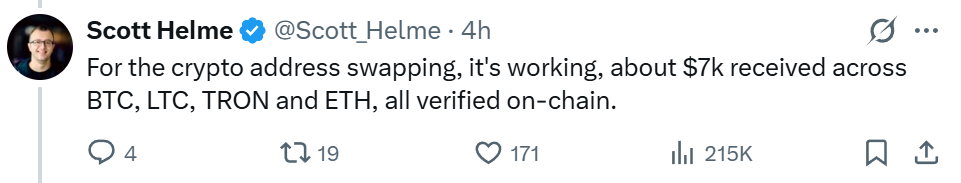
Blockchain records checked by Cointelegraph showed around $7,100 received on November 16 by cryptocurrency addresses linked to the malware. That figure is not a confirmed victim-loss total. StepSecurity separately estimated roughly $6,600 received or held across the wallets and noted that some addresses had activity before the attack. Galaxy Digital researcher Alex Thorn estimated that victims sent around $2,300 in total; he said most Bitcoin receipts appeared to be the attacker’s own funds routed through an exchange back to their wallet.
An OANDA spokesperson, responding on behalf of Coinpass and TMS Brokers, said its security team was reviewing its environment after the incident. The spokesperson said OANDA’s internal systems and infrastructure had not been breached and that it had seen no indication of an impact on client funds or account data. Salesforce said it was investigating unauthorized changes to Optimizely scripts on certain Salesforce websites and was confirming that those scripts were disabled across preview and production instances.
This account reflects reporting originally published November 17, 2026, with statements and analysis added in updates through November 18, 2026. It should not be read as a report of a newly occurring attack.