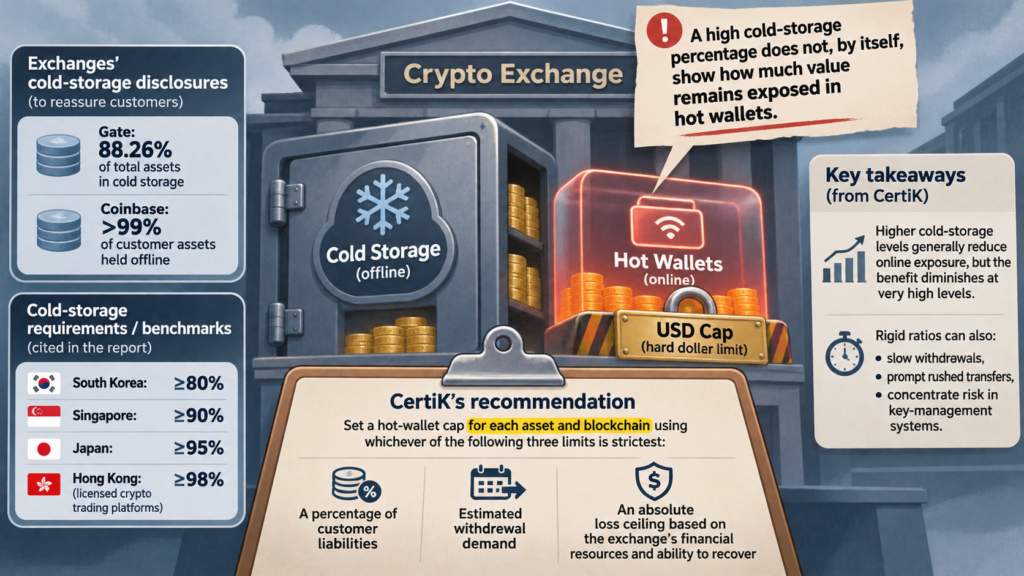
For customers holding assets on an exchange, a high cold-storage percentage does not, by itself, show how much value remains exposed in hot wallets. In a report published November 10, 2026, at 13:18 (UTC+8), ChainCatcher said cybersecurity firm CertiK had recommended hard dollar limits on exchanges’ hot-wallet holdings.
The recommendation followed what the report described as a record-breaking hack of a Binance hot wallet. Exchanges had also been disclosing cold-storage figures to reassure customers: Gate reported holding 88.26% of its total assets in cold storage, while Coinbase said more than 99% of customer assets were held offline.
CertiK’s research team told Cointelegraph that cold storage is a useful measure of online exposure, but not a standalone security score. The report cited requirements or benchmarks of at least 80% of customer crypto assets in cold storage in South Korea, 90% under Singapore guidelines, 95% under Japan’s framework, and 98% for licensed crypto trading platforms in Hong Kong.
CertiK said higher cold-storage levels generally reduce online exposure, but the benefit diminishes at very high levels. Rigid ratios could also slow withdrawals, prompt rushed transfers and concentrate risk in key-management systems. It proposed setting a hot-wallet cap for each asset and blockchain using whichever of three limits is strictest: a percentage of customer liabilities, estimated withdrawal demand, or an absolute loss ceiling based on the exchange’s financial resources and ability to recover.
Separately, Binance said the previous week that it had replenished about 98% of the affected tokens after the hack and would bear the losses itself; it said the remaining tokens had lower liquidity and would take longer to obtain. Elliptic also said hackers linked to North Korea had moved about $430,000 through six newly issued memecoins on NEAR. The report does not establish that this activity was connected to the Binance hack.
Source: chaincatcher.com (originally published 2026-11-10 13:18 UTC+8)