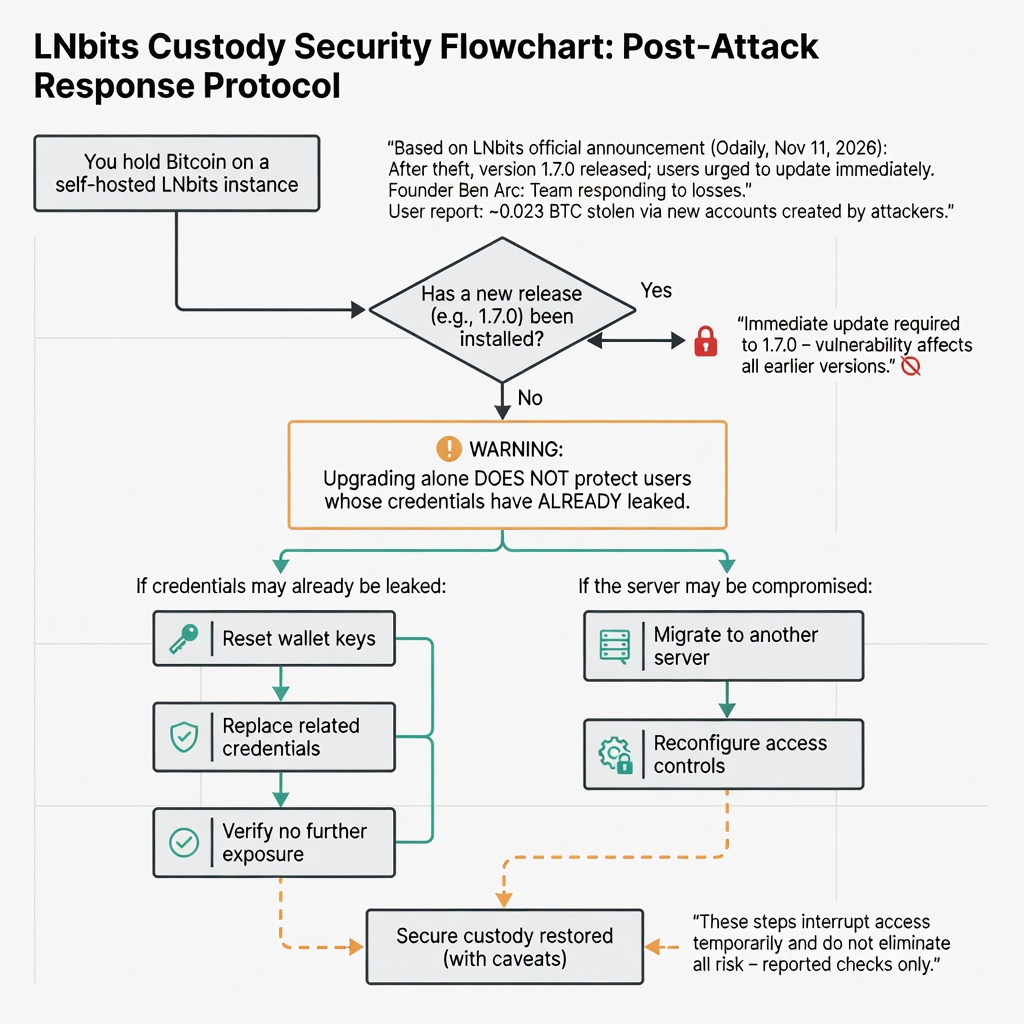
If you hold bitcoin on a self-hosted LNbits instance, the immediate custody question is whether installing a new release is enough, or whether keys and server access may already be outside your control.
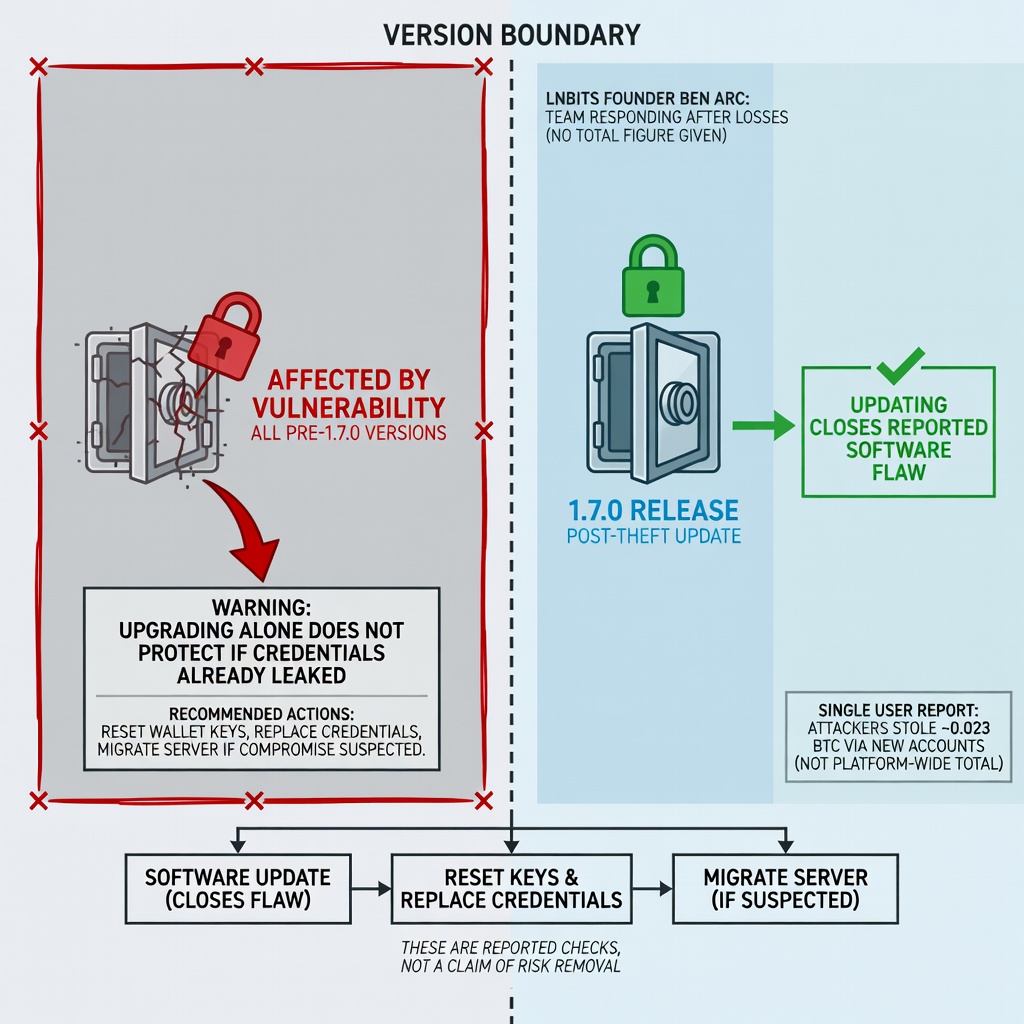
On November 11, 2026, Odaily reported, citing an official LNbits announcement, that the Bitcoin Lightning Network wallet platform LNbits released version 1.7.0 after a recent theft of funds and urged users to update immediately. LNbits warned that the vulnerability affects all earlier versions.
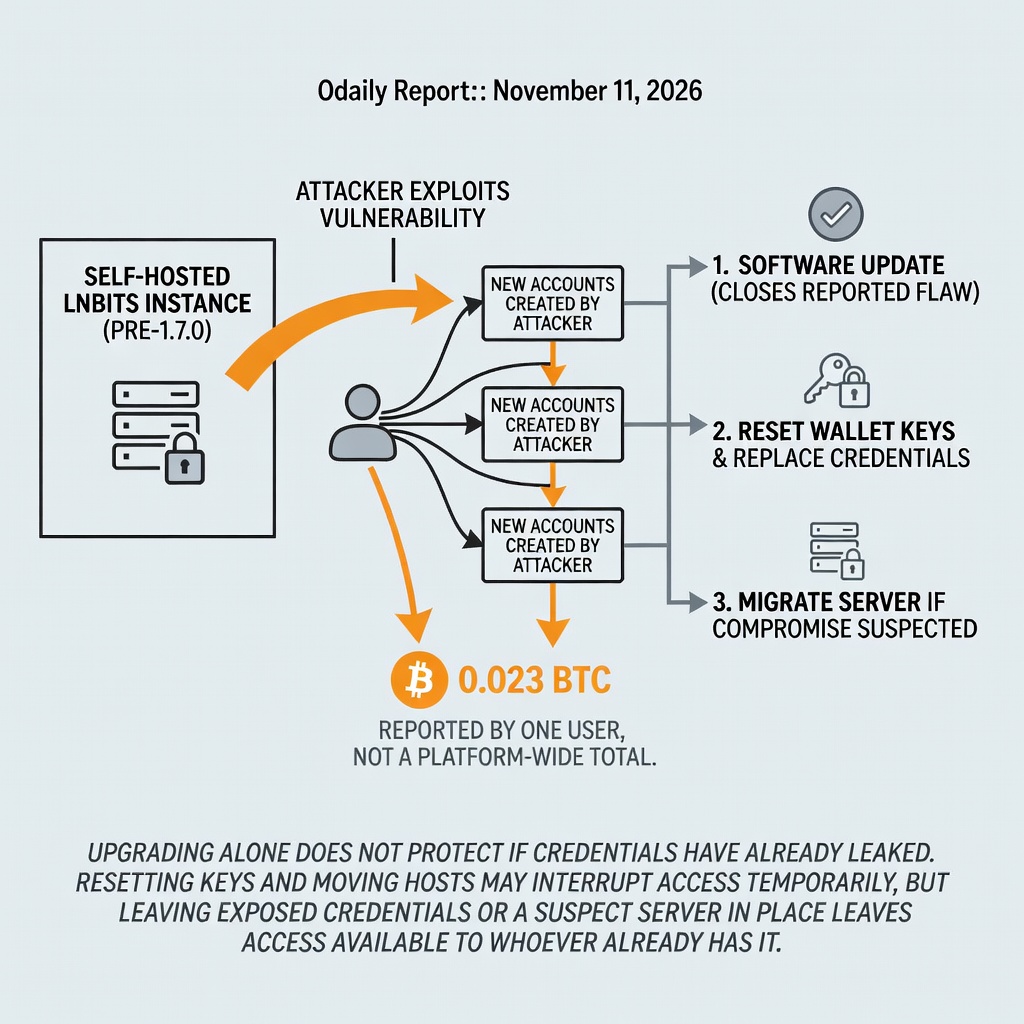
The announcement separates a software update from a credential problem. Upgrading alone does not protect users whose credentials have already leaked. LNbits recommended resetting wallet keys, replacing related credentials, and migrating the server if a compromise of the server is suspected. Updating can close the reported flaw in the software you run. Resetting keys and moving hosts can interrupt access for a time, while leaving exposed credentials or a suspect server in place leaves that access available to whoever already has it. These are reported checks, not a claim that any setup removes all risk.
LNbits founder Ben Arc said that after users and the team suffered losses, the team was working to respond. No total loss figure was given for the team or for users as a group. Separately, one user reported that attackers used their LNbits instance to create new accounts and stole about 0.023 bitcoin. That amount is a single user report, not a confirmed platform-wide total.
Original report: Odaily, November 11, 2026, 09:29 UTC+8.