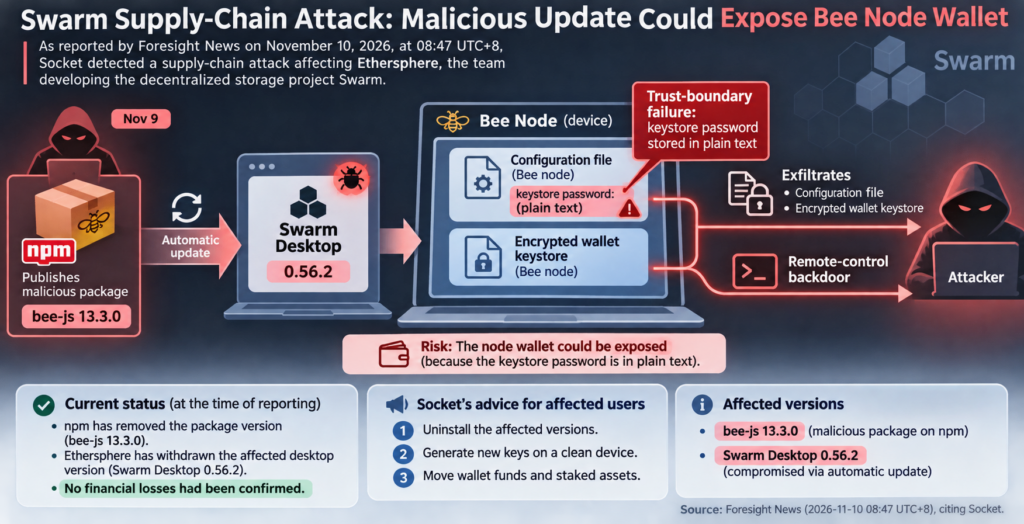
For anyone who ran a Bee node, the concern in this report is whether an affected update exposed the node’s wallet. As reported by Foresight News on November 10, 2026, at 08:47 UTC+8, Socket detected a supply-chain attack affecting Ethersphere, the team developing the decentralized storage project Swarm.
According to Socket, an attacker published a malicious bee-js 13.3.0 package to npm on November 9. An automatic update then distributed a compromised Swarm Desktop 0.56.2. Socket said the malicious code could send a Bee node’s configuration file and encrypted wallet keystore to the attacker. Because the configuration file stored the keystore password in plain text, the node wallet could be exposed. The attack also planted a remote-control backdoor on the device, according to the report.
At the time of reporting, npm had removed the package version and Ethersphere had withdrawn the affected desktop version. No financial losses had been confirmed. Socket advised affected users to uninstall the versions, generate new keys on a clean device, and move wallet funds and staked assets.
Source: foresightnews.pro (originally published 2026-11-10 08:47 UTC+8)