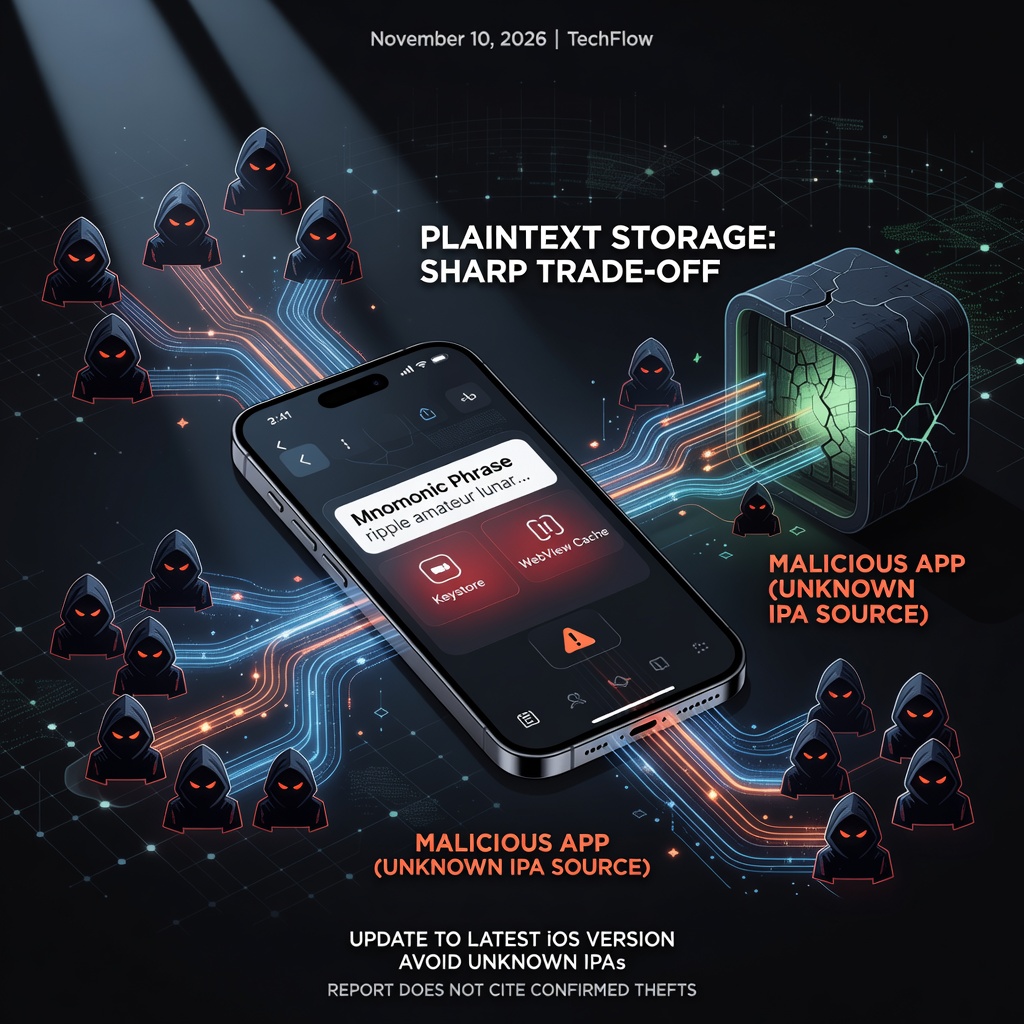
If you keep a self-custody wallet on an iPhone, recovery material has to stay available to you without being easy for other apps to open. Plaintext storage makes that trade-off sharper: the wallet can read the data locally, and so can anything else that can reach the same container.
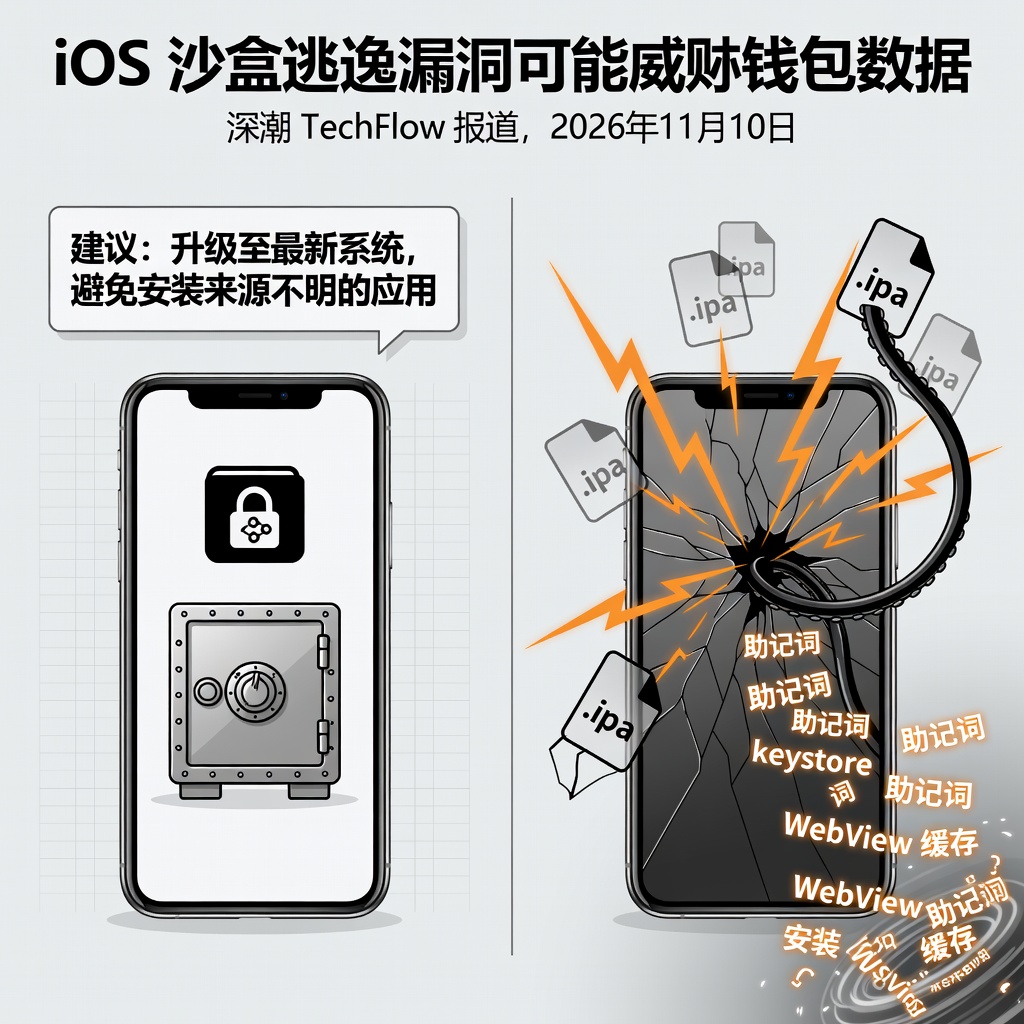
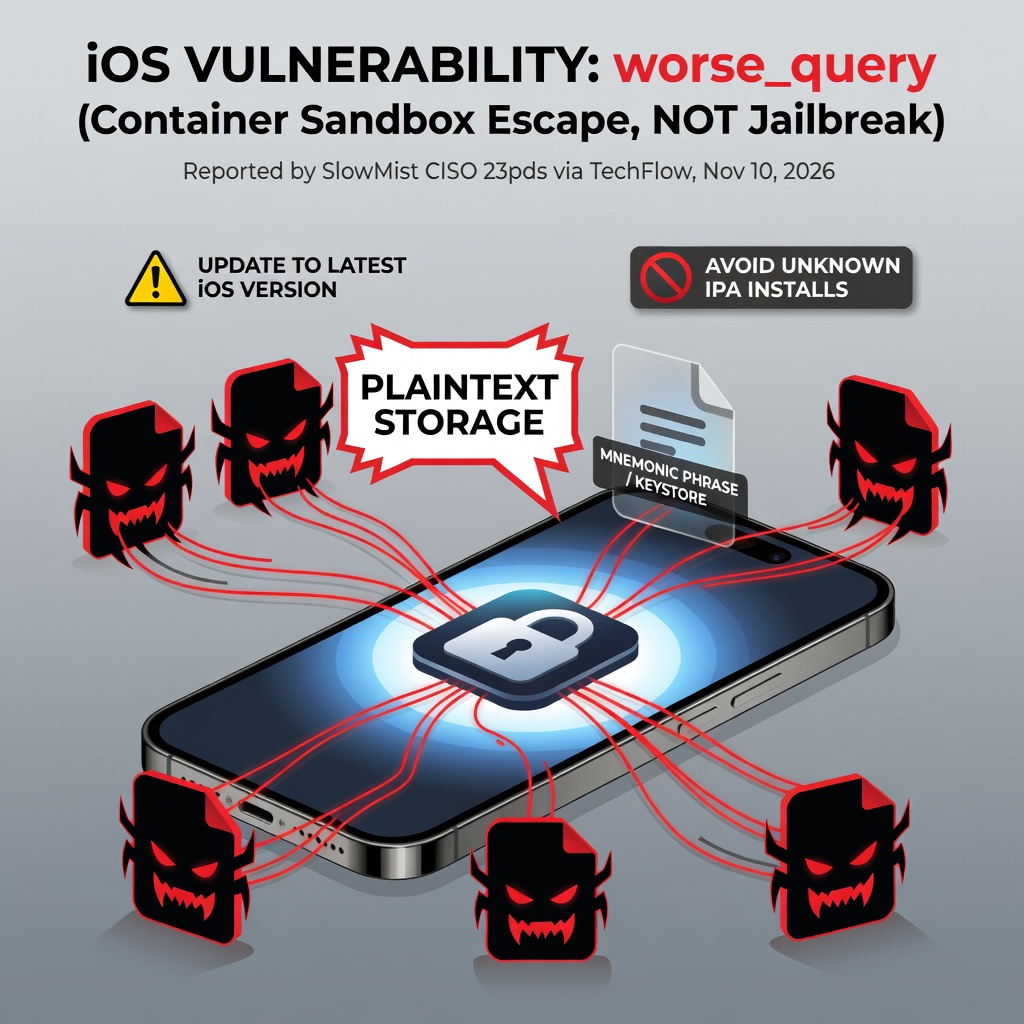
On November 10, 2026, TechFlow reported a warning posted by SlowMist chief information security officer 23pds about an iOS vulnerability named worse_query. He described it as a container sandbox escape, not a jailbreak, and said it may break data isolation between applications.
He stated that the vulnerability itself does not automatically steal assets. The risk he described follows a further action: after a user installs and runs an IPA from an unknown source, a malicious app may be able to read other apps’ containers. If a wallet stores a mnemonic phrase, a keystore, or WebView cache in plaintext on the device, that data could be read.
The checks he suggested are to update the system to the latest version and to avoid installing apps from unknown sources. Those steps narrow one path into local app data. They do not make on-device storage risk-free, and this report does not cite confirmed thefts or measured losses.
Original article (TechFlow, published November 10, 2026, 11:03 UTC+8): https://www.techflowpost.com/zh-CN/newsletter/143839