A wallet’s permissions can limit what a signing key is allowed to do—but they cannot help if the policy permits a transfer the operator did not intend. That is the concern raised by a reported loss of about $6.45 million from a Safe wallet.
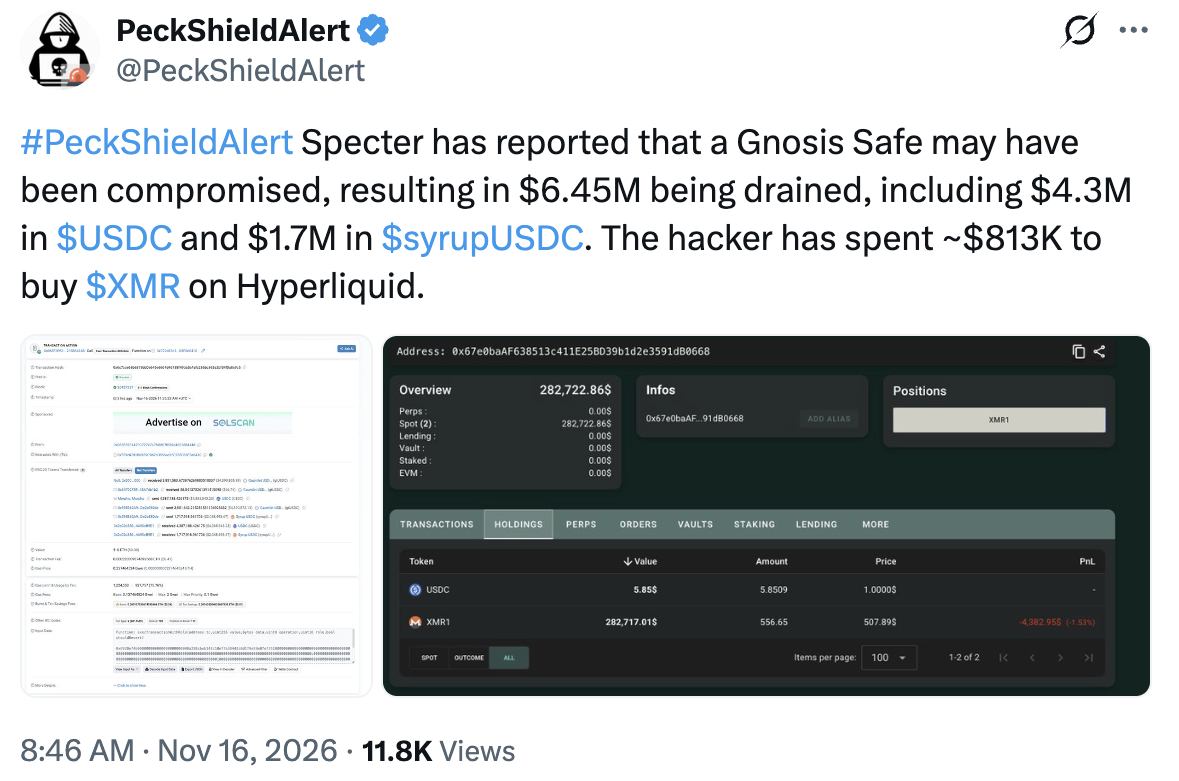
In reporting published on November 17, 2026, Cointelegraph said blockchain records showed approximately 4.39 million USDC and 1.72 million syrupUSDC tokens leaving the wallet in a single transaction on Monday, November 16. PeckShield reported the suspected theft, citing onchain investigator Specter. The wallet owner’s identity had not been established.
Johannes Moormann, co-founder of Zodiac, told Cointelegraph that the transaction passed through the wallet’s Zodiac Roles Modifier. The module checked it against the wallet’s configured permissions and allowed it. Moormann said there was no vulnerability in the module: the transaction came from a long-standing role member’s key that was most likely compromised, while the wallet’s custom policy almost certainly permitted the transfer unintentionally. He said the wallet’s operators controlled its keys and permissions; Zodiac had no access to them and had not helped set them up. Zodiac had not been in contact with the affected team.
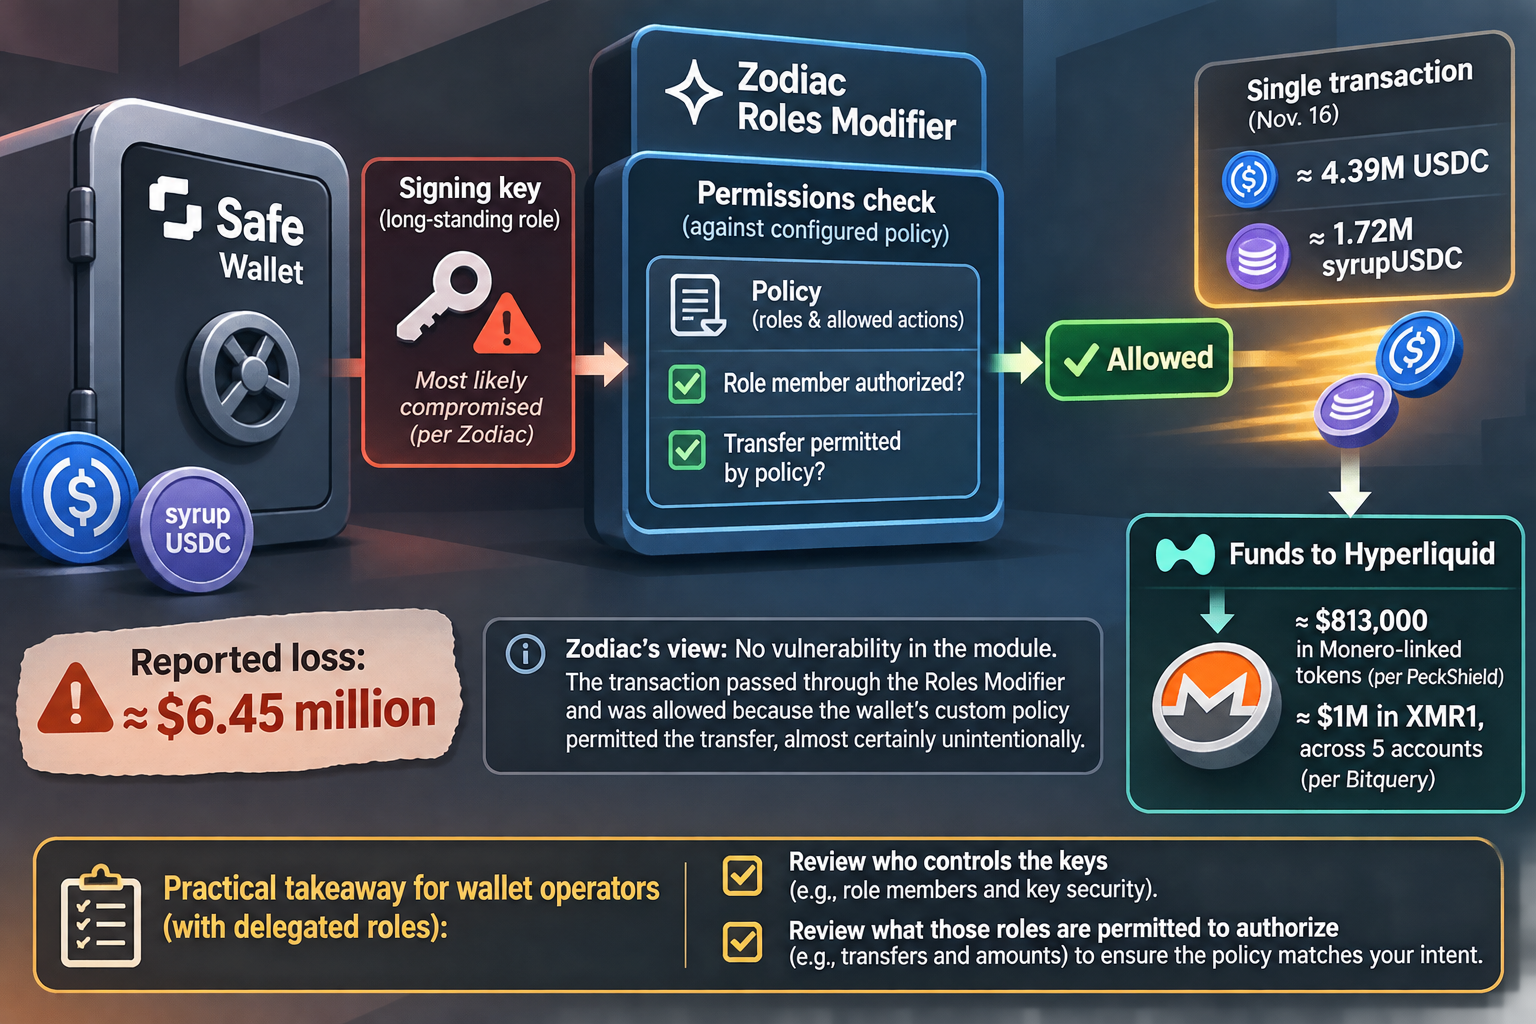
PeckShield also said the attacker used approximately $813,000 to buy Monero-linked tokens on Hyperliquid. Separately, Bitquery traced funds through multiple addresses to Hyperliquid, where it said five accounts bought approximately $1 million in XMR1 tokens. Bitquery noted similarities to fund movements after Monday’s Lighter incident but found no transfers connecting the two wallet groups and could not establish whether the same actor was involved.
The practical distinction is between a module rejecting transactions outside its policy and a policy that allows more than its operators intended. For anyone managing a wallet with delegated roles, the source-supported check is to review both who controls the keys and what those roles are permitted to authorize. Cointelegraph said Safe and Gnosis Guild had not responded to its requests for comment by publication.