Connecting a wallet usually starts with a familiar website. If that domain is no longer under the service’s control, the page can become a phishing site even when the bridge itself has not been described as changed.
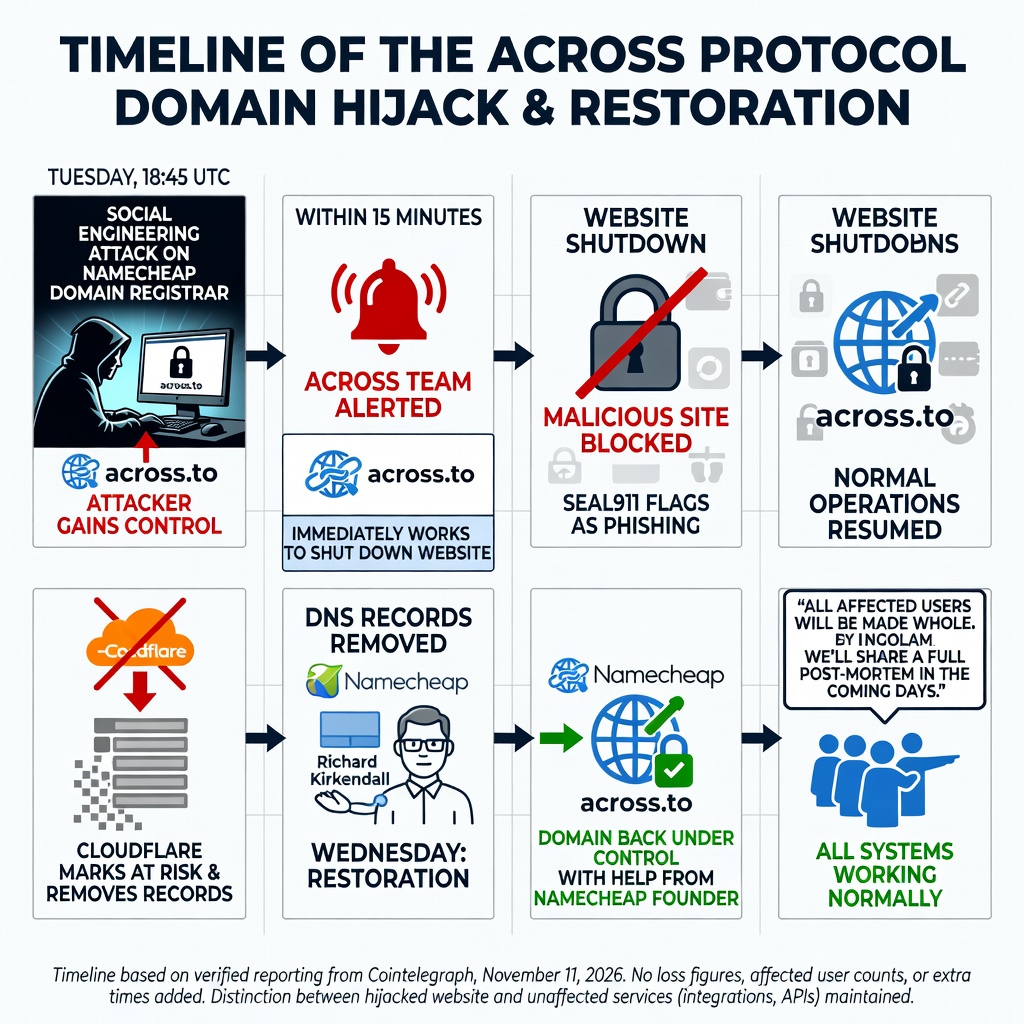
In reporting published on November 11, 2026, Cointelegraph said cross-chain bridge Across Protocol had regained control of its website after a social engineering attack. Across placed the attack on Tuesday and said it let attackers take control of the domain and replace the website with a phishing site.
In a Wednesday post, Across said the across.to domain was back under its control with help from Namecheap founder Richard Kirkendall and that all systems were working normally. “All affected users will be made whole. We’ll share a full post-mortem in the coming days,” the team said on X.
That update followed Across’s Tuesday warning that users should avoid its app amid reports of drained wallets. At the time of the report, the total losses and the number of affected users had not been disclosed.
Across attributed the takeover to a social engineering attack on its domain registrar, Namecheap. The team said an attacker gained control of the domain at approximately 18:45 UTC, that Across was alerted within 15 minutes, and that it immediately worked to shut the website down.
Security response group SEAL911 helped flag the domain as phishing with major wallets. Cloudflare marked it as at risk and later removed its DNS records. Across said some users who visited the domain before the malicious site was fully blocked may have been affected. Third-party integrations and API users were unaffected.
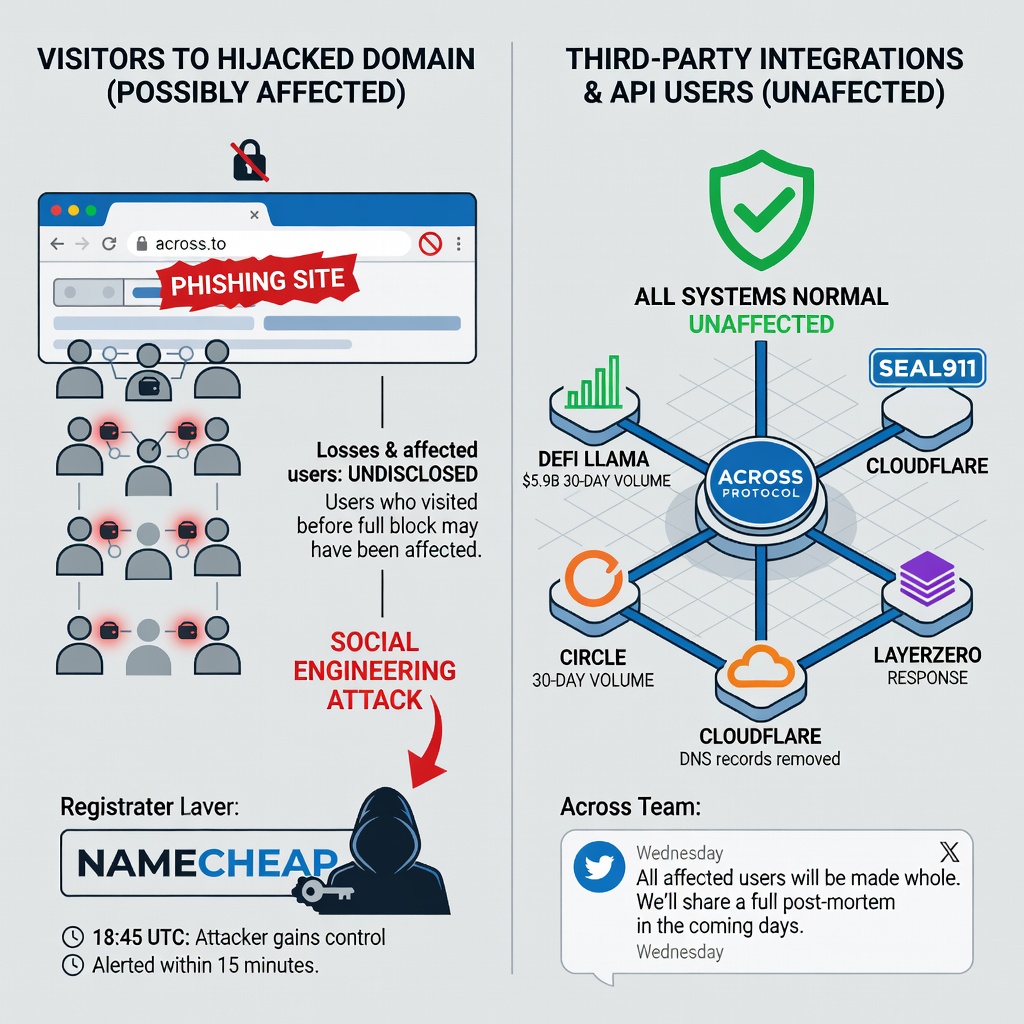
The report described the incident as affecting one of the largest cross-chain bridges by trading activity. According to DefiLlama, Across ranked third by 30-day transfer volume, behind Circle and LayerZero, having processed about $5.9 billion over the period.
The stated risk was limited to people who reached the site while it was under attacker control. Integrations and API users were reported as unaffected, and neither the loss total nor the number of affected users was disclosed. Across said affected users would be made whole and that a fuller post-mortem would follow. Until that account is available, the source-supported distinction is between a hijacked website and services the team said were not affected—not a claim that reconnecting a wallet is risk-free.
Source: cointelegraph.com (originally published 2026-11-11 12:42 UTC+8)