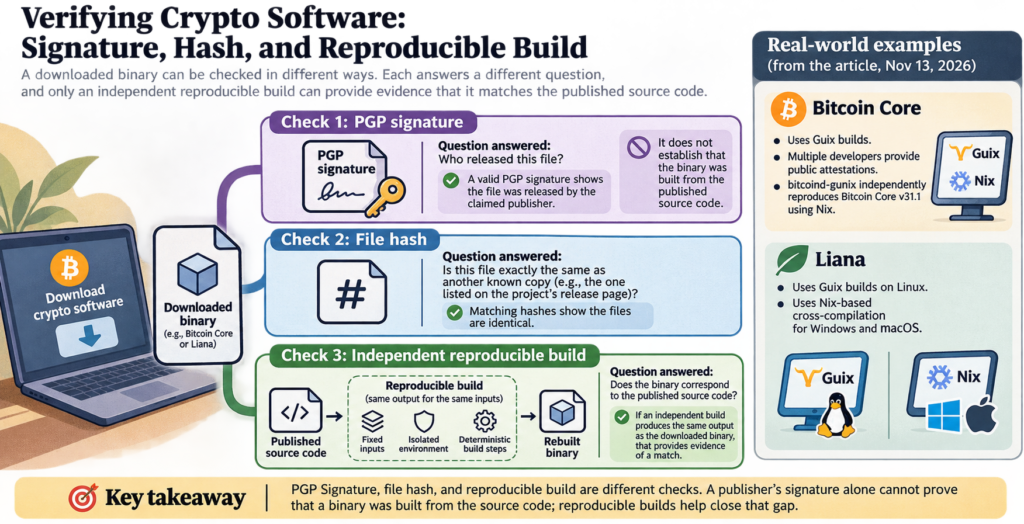
When you download software used to hold or move crypto, a valid PGP signature helps you check who released the file. It does not establish that the binary was built from the published source code.
An article published on November 13, 2026, explains how reproducible builds address that gap: independent builders use fixed inputs, isolated environments and deterministic build steps to check whether they produce the same output. It describes Bitcoin Core’s use of Guix builds with public attestations from multiple developers, and says bitcoind-gunix independently reproduces Bitcoin Core v31.1 using Nix. For Liana, it describes Guix builds on Linux and Nix-based cross-compilation for Windows and macOS.
The practical distinction is between checking a release’s signature, checking a file’s hash, and independently rebuilding it. Each answers a different question. Rebuilding can provide evidence that a binary corresponds to source code; a publisher’s signature alone cannot. The article also discusses commands for those checks, but the supplied material does not include them, so no commands are reproduced here.