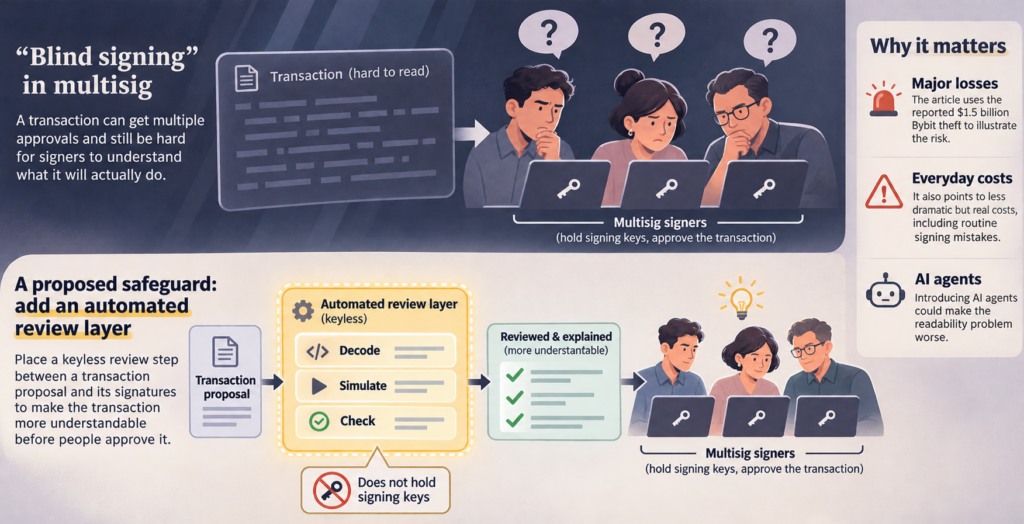
A multisig wallet can require several approvals and still leave signers unable to verify what a transaction will do. That is the holding risk examined in an article published on June 5, 2026: blind signing, where the approval process works as designed but the transaction is difficult for people to interpret.
The article uses the reported $1.5 billion Bybit theft to illustrate its concern. Its argument is that correctly executed multisig approvals do not, by themselves, establish that signers understood the transaction they authorized. It also points to less dramatic costs, including everyday signing mistakes, and warns that introducing AI agents could make the readability problem worse.
As a proposed safeguard, the article suggests placing an automated review step between a transaction proposal and its signatures. That step would decode, simulate and check the transaction without holding signing keys. It is a proposal for making approvals more understandable—not a claim that such a review step was used in the Bybit incident or that it would eliminate signing risk.