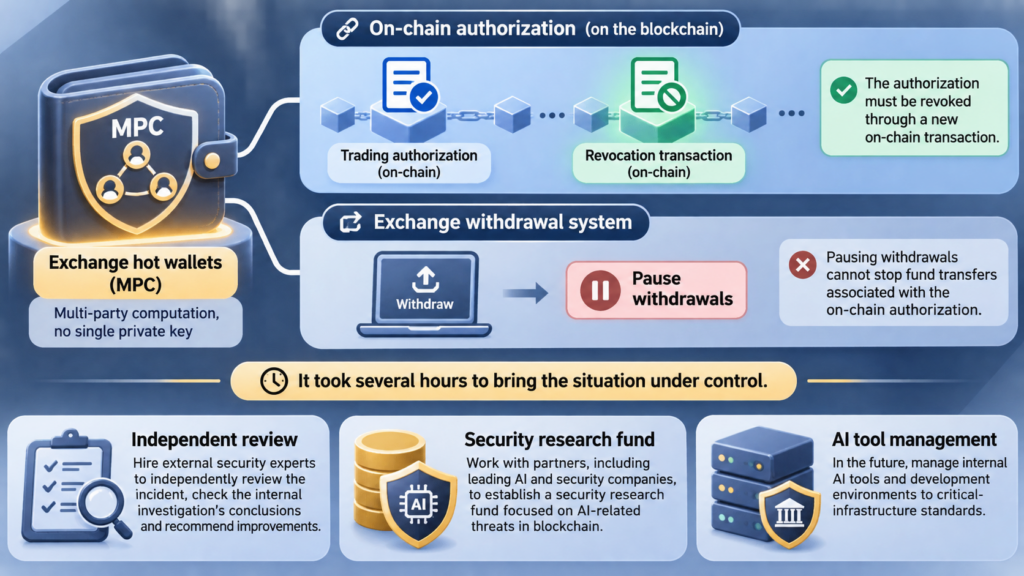
For anyone holding assets on an exchange, the distinction between a withdrawal and an on-chain authorization matters. In remarks reported on November 9, 2026, Binance chief security officer Jimmy Su said the authorization exploited in an October 29 security incident existed on-chain and did not pass through Binance’s withdrawal system. Pausing withdrawals therefore could not stop the associated fund transfers, he said; the authorization had to be revoked through a new on-chain transaction.
Su said Binance’s hot wallets use multi-party computation (MPC), so there was no single private key the team could use directly to revoke the authorization. The team had to devise a revocation process, and it took several hours to bring the situation under control, according to Su. The report did not state a loss amount.
In the same Binance X Space discussion, Su said Binance was hiring external security experts to independently review the incident, check its internal investigation’s conclusions and recommend improvements. He also said Binance was working with partners, including leading AI and security companies, to establish a security research fund focused on AI-related threats in blockchain. Binance planned to manage its internal AI tools and development environments to critical-infrastructure standards in the future, he said.