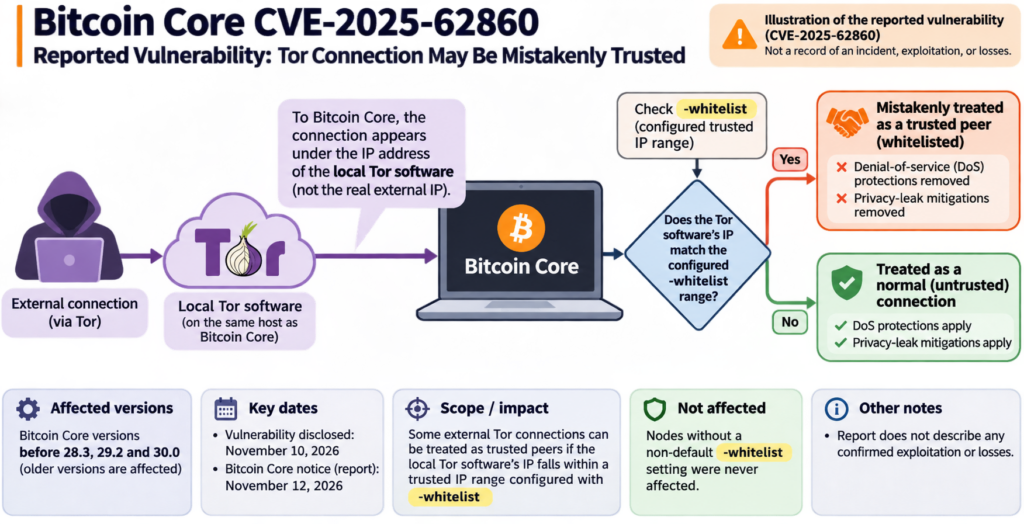
If you run Bitcoin Core through Tor, the relevant setting to check is -whitelist. According to a Bitcoin Core notice reported on November 12, 2026, a medium-severity vulnerability, CVE-2025-62860, could cause some external Tor connections to be treated as trusted peers. The vulnerability was disclosed on November 10, 2026.
The issue affects versions before Bitcoin Core 28.3, 29.2 and 30.0. An external connection arriving through Tor appears to Bitcoin Core under the IP address of the local Tor software. If that address falls within a trusted IP range configured with -whitelist, Bitcoin Core can mistakenly whitelist the connection. That removes denial-of-service protections and privacy-leak mitigations normally applied to those connections.
The notice says nodes without a non-default -whitelist setting were never affected. The report does not describe any confirmed exploitation or losses.